Home Top Ad

Responsive Ads Here

Google is restarting the Wear OS 5 rollout on older Pixel Watch models It has previously been paused because it was bricking devices Pix...

  • Google is restarting the Wear OS 5 rollout on older Pixel Watch models
  • It has previously been paused because it was bricking devices
  • Pixel Watch 1 and 2 users will see the rollout starting now

Google has confirmed that it's restarting the rollout of Wear OS 5 for Pixel Watch 1 and 2 owners, weeks after the update was pulled because the new software was bricking devices.

Google paused the Wear OS 5 update in late September after users reported that the update was bricking their older-generation Pixel Watch models. At the time, Google told us it had put the update on hold while it looked for a solution.

In a community post on November 12, Google confirmed that the rollout is back underway.

"Pixel Watch 1, Pixel Watch 2, and Pixel Watch 3 devices will receive the November 2024 software update, with the next update planned for March 2025," Google stated, adding that with this update "Pixel Watch 1 and 2 users will resume receiving the Wear OS 5 upgrade starting today (November 12.)"

Google says Pixel Watch users can expect the update to land over the coming week depending on carrier and device, and they'll get a notification on their watch once the update is available.

Wear OS 5 comes to older Pixel Watch models

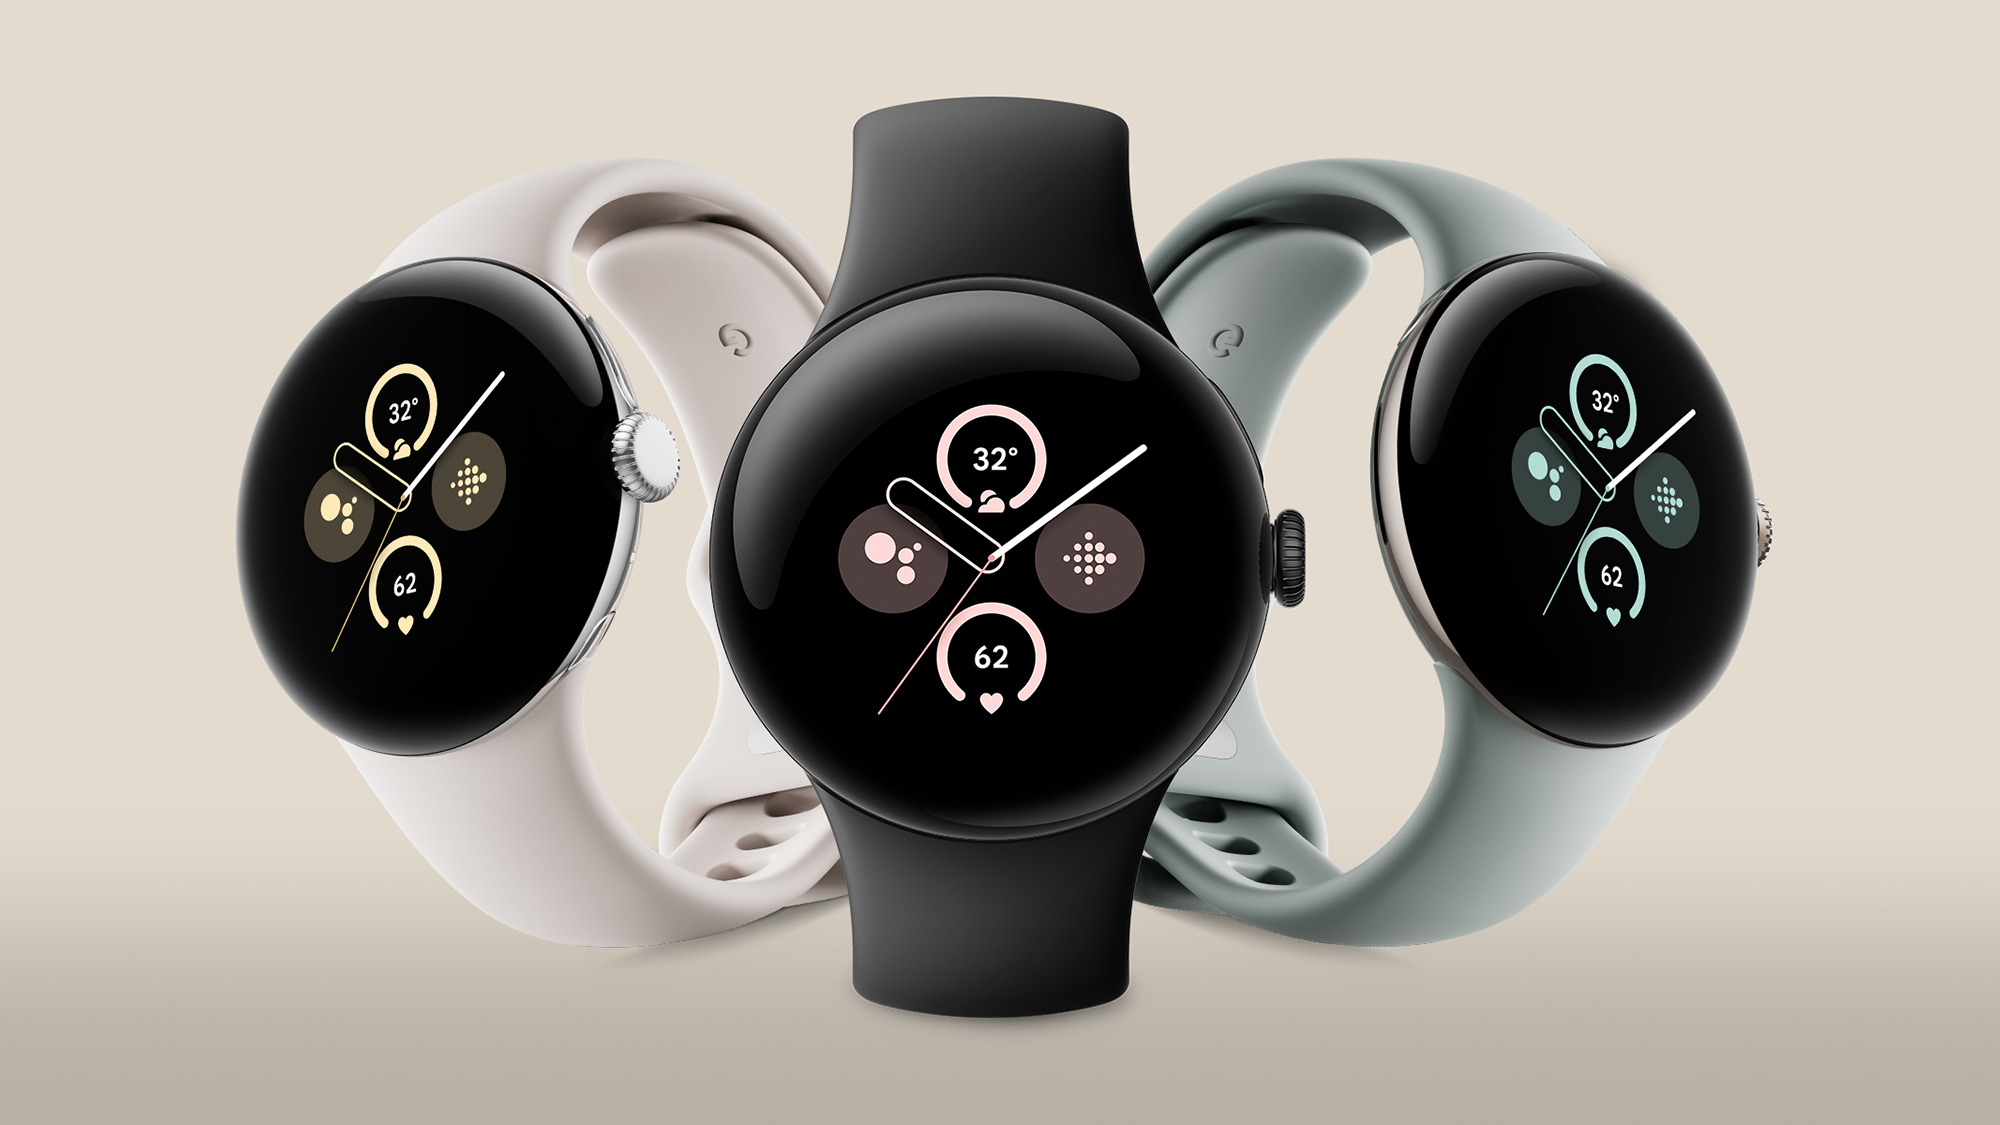
Google Pixel Watch 2 models

(Image credit: Google)

The Wear OS 5 rollout is great news for owners of the Pixel Watch and Pixel Watch 2, which are still some of the best Android smartwatch options out there despite the launch of the Pixel Watch 3 earlier this year. Users can expect improved performance and battery life, as well as new running metrics such as ground contact time and vertical oscillation.

Not only is it great news for existing Pixel Watch customers, it could also give a boost to Pixel Watch sales ahead of the Black Friday deals event. We expect to see big savings on Pixel Watch 1 and 2 models (the Pixel Watch 2 is already $100 off at Amazon), and now prospective customers know they're getting the latest Android wearable software if they decide to go for an older model.

You may also like


from TechRadar - All the latest technology news https://ift.tt/gRaQFzn

Just before the 2024 general election was announced, the UK government was looking to bring in tougher rules on ransomware payments, includ...

Just before the 2024 general election was announced, the UK government was looking to bring in tougher rules on ransomware payments, including the potential to ban ransom payments entirely. The justification? A decisive action to cut off the business model of cyber extortionists.

But the message around ransom payments is contradictory to say the least. In the UK, the NCSC has made it abundantly clear that businesses should not pay ransoms. Yet, insurance policies recommended by the government's Cyber Essentials scheme clearly state that they provide cover for extortion payments. Ultimately though, this directly funds cybercriminal activity and enables it to gain momentum.

So, what are the benefits and drawbacks of banning ransomware payments, what alternatives can be considered and what role does the cyber insurance industry play in tackling this threat?

To pay or not to pay

Earlier this year, French hospital, CHCSV, refused to pay a ransomware demand, despite suffering severe operational disruption. Meanwhile, other organizations that have fallen victim, such as Change Healthcare in the US, have gone in a different direction, with this particular private healthcare firm paying $22m to attackers.

The difference here is that one victim falls within the public sector, while the other doesn’t, and when public sector organizations pay ransom demands, it ultimately comes out of tax payers’ money. It’s for this reason, among others, that several states in the US have already made it illegal for public sector organizations to pay extortion payments.

However, there appears to be less public transparency in the UK on whether companies pay ransomware demands. While the US has official government data specific to ransomware payments, the UK lacks official reporting as most of the data available comes from industry reports. For instance, a report from Censornet revealed 85% of SMEs report paying a ransomware demand, while research from Cohesity found that 69% had paid a ransom in the last year.

But not paying can cost businesses more in the long run. For example, last year, MGM Resorts didn’t pay its attackers but has since revealed costs of up to $110m. Similarly, the WannaCry incident, which affected thousands of NHS hospitals and surgeries in 2017, is reported to have cost £92 million in recovery.

While ransomware victims continue to play this game of ‘will they, won’t they’, according to Mordor Intelligence and Fortune Business Insights the cyber insurance market in the UK is estimated to be $1.35bn in 2024 and $20.88 billion globally, with new policies continually being established as businesses scramble to insure themselves against the inevitable.

Insurers, unsurprisingly, will usually look for the lowest cost option when dealing with the fallout of a ransomware attack: paying the ransom demands. But doing so funds this global cybercrime pandemic. It’s therefore little surprise that ransomware payments, according to Chainalysis, broke the $1bn mark in 2023.

So, while some believe ransomware is becoming more prevalent due to better targeting by cyber criminals, it’s perhaps worth considering whether it’s any coincidence that as the insurance industry grows, so too does the cybercrime landscape.

What other choice do we have?

Despite these somewhat muddied waters, the correct response to ransomware attacks is clear: paying demands should almost always be a last resort. The only exception should be where there is a risk to life. Paying because it’s easy, costs less and causes less disruption to the business is not a good enough reason to pay, regardless of whether it’s the business handing cashing out or an insurer.

However, while a step in the right direction, totally banning ransom payments addresses only one form of attack and feels a bit like a ‘whack-a-mole’ strategy. It may ease the rise in attacks for a short while, but attackers will inevitably switch tactics, to compromising business email perhaps, or something we’ve not even heard of yet.

So, what else can be done to slow the rise in ransomware attacks? Well, we can consider a few options, such as closing vulnerability trading brokers and regulating cryptocurrency transactions. To pick on the latter as an example, most cybercrime monetizes through cryptocurrency, so rather than simply banning payments, it could be a better option to regulate the crypto industry and flow of money.

Alongside this kind of regulatory change, governments could also consider moving the decision of whether to pay or not to an independent body. This would ensure the decision is made regardless of cost and instead based on risk to life and disruption to critical services. Though whether a court, or other independent body, could make these decisions quick enough is up for debate.

Insurance and cyber security can go hand in hand

Digital transformation was expedited during the pandemic and on top of that, extortion based cyber-attacks have been spurred on by cryptocurrency, all within a short time frame.

Meanwhile, the biggest challenge for insurers in today’s digital environment is their lack of data. This perfect storm explains why the insurers are continually adapting requirements and increasing premiums at an escalated pace.

But it’s important to remember that being insured can make the business more of a target because cyber criminals know they may get their ransom payment, fueling this never-ending cycle. It’s therefore essential that businesses adopt a cybersecurity posture that provides them with the best possible protection, insured or not. In fact, opting for an insurer who understands risk based on data can help make a business’ cyber strategy more secure.

For example, insurers who understand risk based on data often require businesses to adopt many different technologies and processes to reduce said risk, for example the use of cloud backup systems, multi-factor-authentication and advanced endpoint detection and response solutions.

In fact, the full list of recommendations these insurers require are typically a subset of those that cybersecurity professionals and cybersecurity frameworks also recommend. And while insurers are focused on reducing the potential of a financial claim, the cybersecurity industry is focused on reducing the risk of any cyberattack, so following these recommendations will inevitably be a positive step for the business.

A match made in cyber heaven?

The relationship between cyber insurance and cybersecurity is inseparable, and these two industries are fast becoming a marriage of convenience. However, there remains one significant obstacle in this becoming a happy and truly fulfilling marriage. The funding of cybercrime through the payment of ransomware demands by insurers needs to stop (unless in exceptional circumstances!).

We've featured the best malware removal tools.

This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro
from TechRadar - All the latest technology news https://ift.tt/tYmaqOJ

Sony is discontinuing its PlayStation Camera adapter for PS5 The accessory is offered for free on the official PlayStation website Playe...

  • Sony is discontinuing its PlayStation Camera adapter for PS5
  • The accessory is offered for free on the official PlayStation website
  • Players will have until November 26, 2024 to claim one

Sony is set to discontinue distribution of its free PlayStation VR camera adapter for PS5 in just two weeks' time.

The adapter is required for PlayStation Camera compatibility on PS5, thus allowing owners of the original PlayStation VR headset to use it and play its games on Sony's current-generation console.

As per the accessory's official support page, you'll have until November 26, 2024 "or until supplies last" before Sony discontinues it for good. If you still need to claim one before then, you can do so by signing into your PlayStation account on the website and filling out a brief form. Sony will then ship the camera adapter to you at no cost.

On the face of it, it does seem like pretty terrible news. Outside of any potential firmware updates in the future, the PSVR 2 headset is not backwards compatible with original PlayStation VR games.

After November 26, you'll need to rely on third-party adapters or keep a PS4 on hand if you'd ever like to play titles like Resident Evil 7: Biohazard, Ace Combat 7: Skies Unknown or Wipeout Omega Collection in VR. And sadly, no; bizarrely, the PS5 HD Camera also isn't compatible with the original PlayStation VR.

At the same time, it's understandable why Sony would move to discontinue the adapter eventually. In all likelihood, it probably hasn't been in active production for some time, and the amount of folks who use the original PlayStation VR headset on PS5 likely isn't astronomical.

Hopefully, then, Sony can help offset the loss of the adapter with some strong updates to PSVR 2. Backwards compatibility is a must at this point, and with Sony recently enabling PC support for PSVR 2, having the option to play original PlayStation VR titles on it doesn't seem like too much of a stretch to offer.

You might also like...


from TechRadar - All the latest technology news https://ift.tt/HBCWnwi

There’s no denying the impact AI is already having on data centers and energy use. If left unchecked, the situation is only going to get wo...

There’s no denying the impact AI is already having on data centers and energy use. If left unchecked, the situation is only going to get worse. A recent IDC report reveals that with AI adoption skyrocketing, the energy needed to support AI workloads is set to soar, with data center electricity consumption expected to more than double between 2023 and 2028. AI-driven workloads alone are projected to grow at a staggering compound annual growth rate (CAGR) of 44.7% through 2027, with energy demands reaching a massive 146.2 TWh. The implications are stark - data centers, which already account for 46% of enterprise energy spend, could soon become unsustainable.

That, of course, cannot happen. But with AI workloads rapidly increasing, data centers have to evolve quickly and manage the prospect of a new energy crisis, with rising electricity prices driven by geopolitical instability in the Middle East. The growing influence of AI tools across industries - from healthcare to financial services - is undeniable. However, an AI-powered search uses 100 times more energy than a non-AI-powered search, while building foundational AI models can consume enough energy to power 20,000 homes for six months.

A solution?

An Atlantic Ventures report, Improving Sustainability in Data Centers 2024, suggests a solution, revealing how next-generation data center architectures, like hyperconverged infrastructure (HCI), can reduce energy consumption, lower carbon emissions, and drive cost savings across the EMEA region. In just six years, the report finds that modernizing data centers with HCI could save up to 19 million tCO2e in the EMEA region, equivalent to the emissions of almost 4.1 million cars. It could also save €25 billion by 2030 from improved energy and operational efficiencies.

As organizations integrate AI across operations and come to terms with the sheer scale of energy consumption, HCI could reduce the risk of spiraling costs and ensure sustainability goals are not missed. But it’s not just about HCI, it's about how organizations work with AI. Focus should shift to optimising where and how AI workloads are processed, using modernisation to manage workloads more intelligently. This makes so much more sense than to just keep building more energy-efficient data centers.

This is important, as we have to take into account how AI works and where the demands for power are going to increase. While many organizations are captivated by the energy consumption required to train foundational AI models, for example, it is inferencing - the real-time decision-making AI performs - where the bulk of the energy is spent.

Foundational model training happens once but inferencing is a continuous process that happens millions of times, especially with AI-driven applications like fraud detection or predictive maintenance. Optimizing inferencing, particularly at the edge, could be the silver bullet data centers need to manage AI energy demands more efficiently.

Turning to renewable energy

As the IDC report suggests, more data center providers need to turn to renewable energy sources, but they also need to rethink their infrastructure. Hybrid cloud, edge computing, and on-premise systems offer a way to balance AI’s energy demands by distributing workloads more intelligently.

Processing data closer to its source with edge computing, for example, reduces the energy needed to transfer large datasets back and forth from centralized servers. Meanwhile, hybrid cloud computing environments can handle the computationally intense AI training tasks, leaving real-time inferencing to occur on-premise or at the edge.

Edge computing also plays a pivotal role by processing data closer to where it’s generated, such as in retail stores or IoT devices. This not only improves response times but also significantly reduces the energy required for inferencing.

Modern infrastructure is crucial to managing AI’s energy demands and a containerized platform, designed to handle both CPUs and GPUs, is necessary to run AI workloads efficiently. Storage also becomes critical, as AI typically deals with unstructured data like files and objects. By investing in high-performance storage systems and optimized compute stacks, businesses can significantly reduce the energy required to run AI applications.

Moreover, the ability to measure and manage energy consumption is critical. Platforms that provide real-time visibility into energy use enable data centers to optimize every stage of AI processing - from training to inferencing. Even a 10% improvement in energy efficiency, according to the IDC report, can lead to substantial savings.

Real-time decision-making

Rather than focusing solely on the immense energy costs of training foundational models, businesses need to pay attention to how often these models are used in real-time decision-making. Compressing models, refining their structure, and running them on platforms designed for efficiency will be key in reducing AI’s overall energy footprint. For example, we have developed container platforms and high-performance storage solutions specifically tailored for AI inferencing, offering businesses a way to optimize their AI workloads and temper their energy demands.

The true cost of AI is no longer just about performance and innovation, it’s about the energy required to sustain it. As organisations ramp up their AI initiatives, the question isn’t whether they can afford to invest in AI but whether they can afford the energy it consumes. With hybrid infrastructure and a focus on efficient inferencing, businesses have a way to temper this energy surge. Otherwise, those that ignore this reality may soon find their data centers at the mercy of an AI energy crisis.

We've featured the best colocation providers.

This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro


from TechRadar - All the latest technology news https://ift.tt/lBSH2ck

Search engines all hide their indexing, ranking, and sorting algorithms under lock and key. During the early stages of the most popular sea...

Search engines all hide their indexing, ranking, and sorting algorithms under lock and key. During the early stages of the most popular search engine – Google – ranking signals were relatively simple. These were the days where almost all that was needed were keywords and backlinks.

If you were to ask how many ranking factors Google today has, the honest answer is that no one knows exactly. But most SEO professionals will tell you there’s well over 200 of them.

Clearly, search engines have become significantly more complex. Part of the reason is that the web has become more complicated and much more vast. Search engines are also more complex today because people are always trying to reverse engineer the hidden ranking factors for their own benefit.

Do search engines themselves need proxies?

If you were to build a search engine from scratch today, you would need proxy servers to make it function properly. The underlying technology of a search engine is relatively simple. It runs an automated script that crawls through a website, downloads the HTML, and analyzes the content.

Assuming the content is deemed relevant, it’s added to an index. Users can then use the search bar to run through the index to find the content they need. Of course, the internet is now so vast and advanced that such a simplistic search engine would be considered a failure.

Since a crawler needs to send thousands or even millions of requests to a website to index every piece of content, it’s likely your regular IP address would get banned. Additionally, some content may only be accessible if you’re from a particular country or region, making proxies a necessity.

Established search engines like Google are not banned by websites as nearly everyone wants their content indexed. They still need to acquire location-based content, but they likely use their own servers instead of third-party proxy providers - although we can’t be certain.

How proxies impacted search engines

Then there’s the other end of the spectrum. SEO professionals and enthusiasts have always wanted to figure out how search engines rank websites and what influences the top positions.

If you were a regular user, that would be impossible to figure out. Although Google provides guidelines, most of them are vague (such as “produce good content”). SEO professionals, however, have figured that they can scrape search engines at scale, and add internal data from websites to start gaining insights into ranking factors.

Proxies have to be used, however, as most search engines quickly ban users that are sending too many requests. Additionally, localized content won’t be served effectively without hundreds of IP addresses.

As a result, SEO professionals created dedicated tools (that are also sold to other professionals) to understand how and why search engines rank some content over others. Some of these insights can be quite apt and direct.

A great example of understanding and abusing ranking systems was the SEO contest held way back in 2018. Someone managed to rank a rhinoplasty website for English search results, but the entire website was written in Latin.

Search engines, of course, know that there are tools that purportedly showcase ranking factors. So, if the content is too accurate, search engines have to tweak their algorithms to avoid people from abusing rankings.

Even if it’s used by legitimate SEO use cases, people knowing too much about how search engines rank content can cause issues. The result is search engines have to play a constant cat-and-mouse game.

And that cat-and-mouse game is only really possible because of large-scale data collection from search engines, only made possible by proxies. So, in the end, proxies have a great deal of influence over the way search engines function.

It’s all too easy to think that proxies are negative – in that they reveal some sort of secret ranking system and allow people to abuse it. But many of the changes and tweaks that have been made to the algorithms over the years have been with the idea of improving search results.

In some sense, SEO tools, and web data collection with proxies, provide indirect competition to search engines. They don’t take away the revenue of these companies. But they do nudge them to constantly improve and tweak ranking algorithms – benefiting everyone in the long run.

Link!

This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro


from TechRadar - All the latest technology news https://ift.tt/42rINXu

Good morning! Let's play Connections, the NYT's clever word game that challenges you to group answers in various categories. It can...

Good morning! Let's play Connections, the NYT's clever word game that challenges you to group answers in various categories. It can be tough, so read on if you need clues.

What should you do once you've finished? Why, play some more word games of course. I've also got daily Wordle hints and answers, Strands hints and answers and Quordle hints and answers articles if you need help for those too.

SPOILER WARNING: Information about NYT Connections today is below, so don't read on if you don't want to know the answers.

NYT Connections today (game #519) - today's words

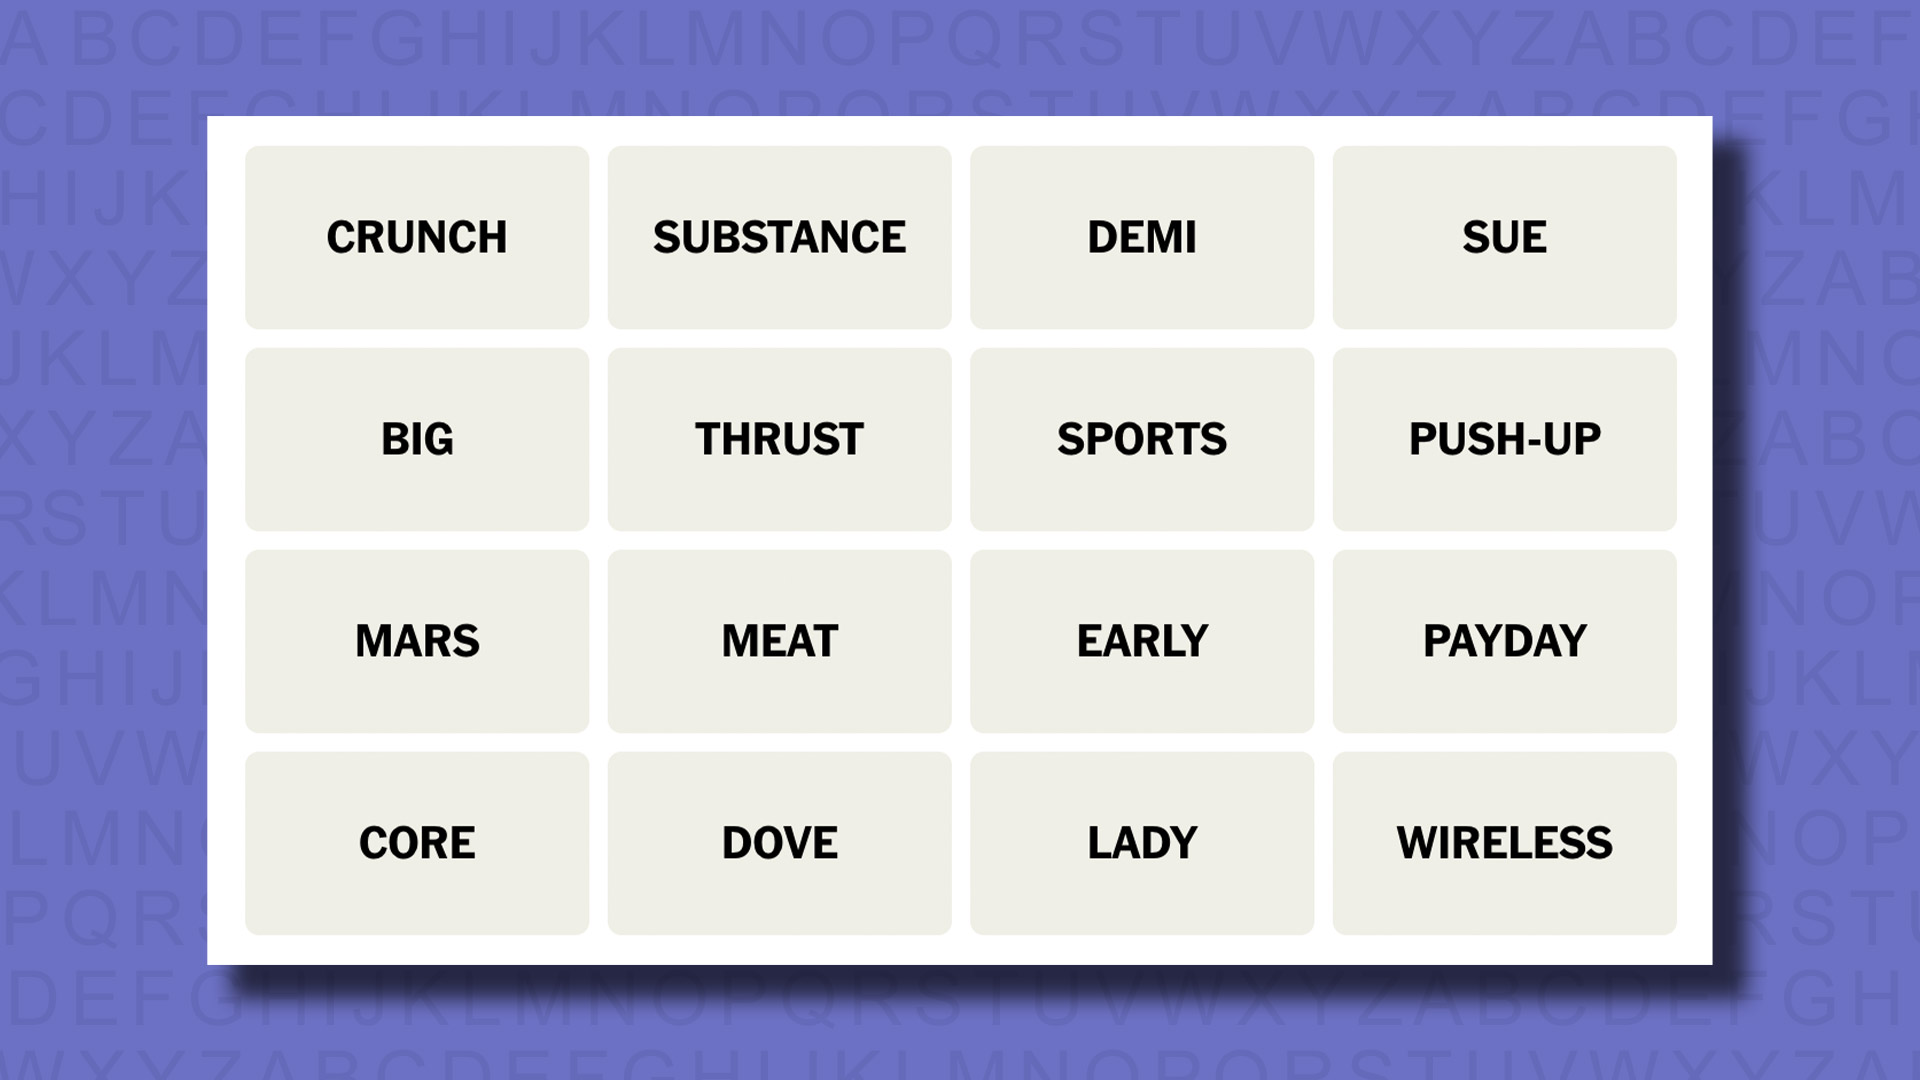
NYT Connections hints for game 519 on a purple background

(Image credit: New York Times)

Today's NYT Connections words are…

  • CRUNCH
  • SUBSTANCE
  • DEMI
  • BIG
  • THRUST
  • SPORTS
  • MARS
  • MEAT
  • EARLY
  • CORE
  • DOVE
  • LADY
  • SUE
  • PUSH-UP
  • PAYDAY
  • WIRELESS

NYT Connections today (game #519) - hint #1 - group hints

What are some clues for today's NYT Connections groups?

  • Yellow: Candy favorites
  • Green: Central point
  • Blue: Gives you support (possibly!)
  • Purple: Blank [avian]

Need more clues?

We're firmly in spoiler territory now, but read on if you want to know what the four theme answers are for today's NYT Connections puzzles…

NYT Connections today (game #519) - hint #2 - group answers

What are the answers for today's NYT Connections groups?

  • YELLOW: CHOCOLATE BARS
  • GREEN: GIST
  • BLUE: KINDS OF BRAS
  • PURPLE: ___ BIRD

Right, the answers are below, so DO NOT SCROLL ANY FURTHER IF YOU DON'T WANT TO SEE THEM.

NYT Connections today (game #519) - the answers

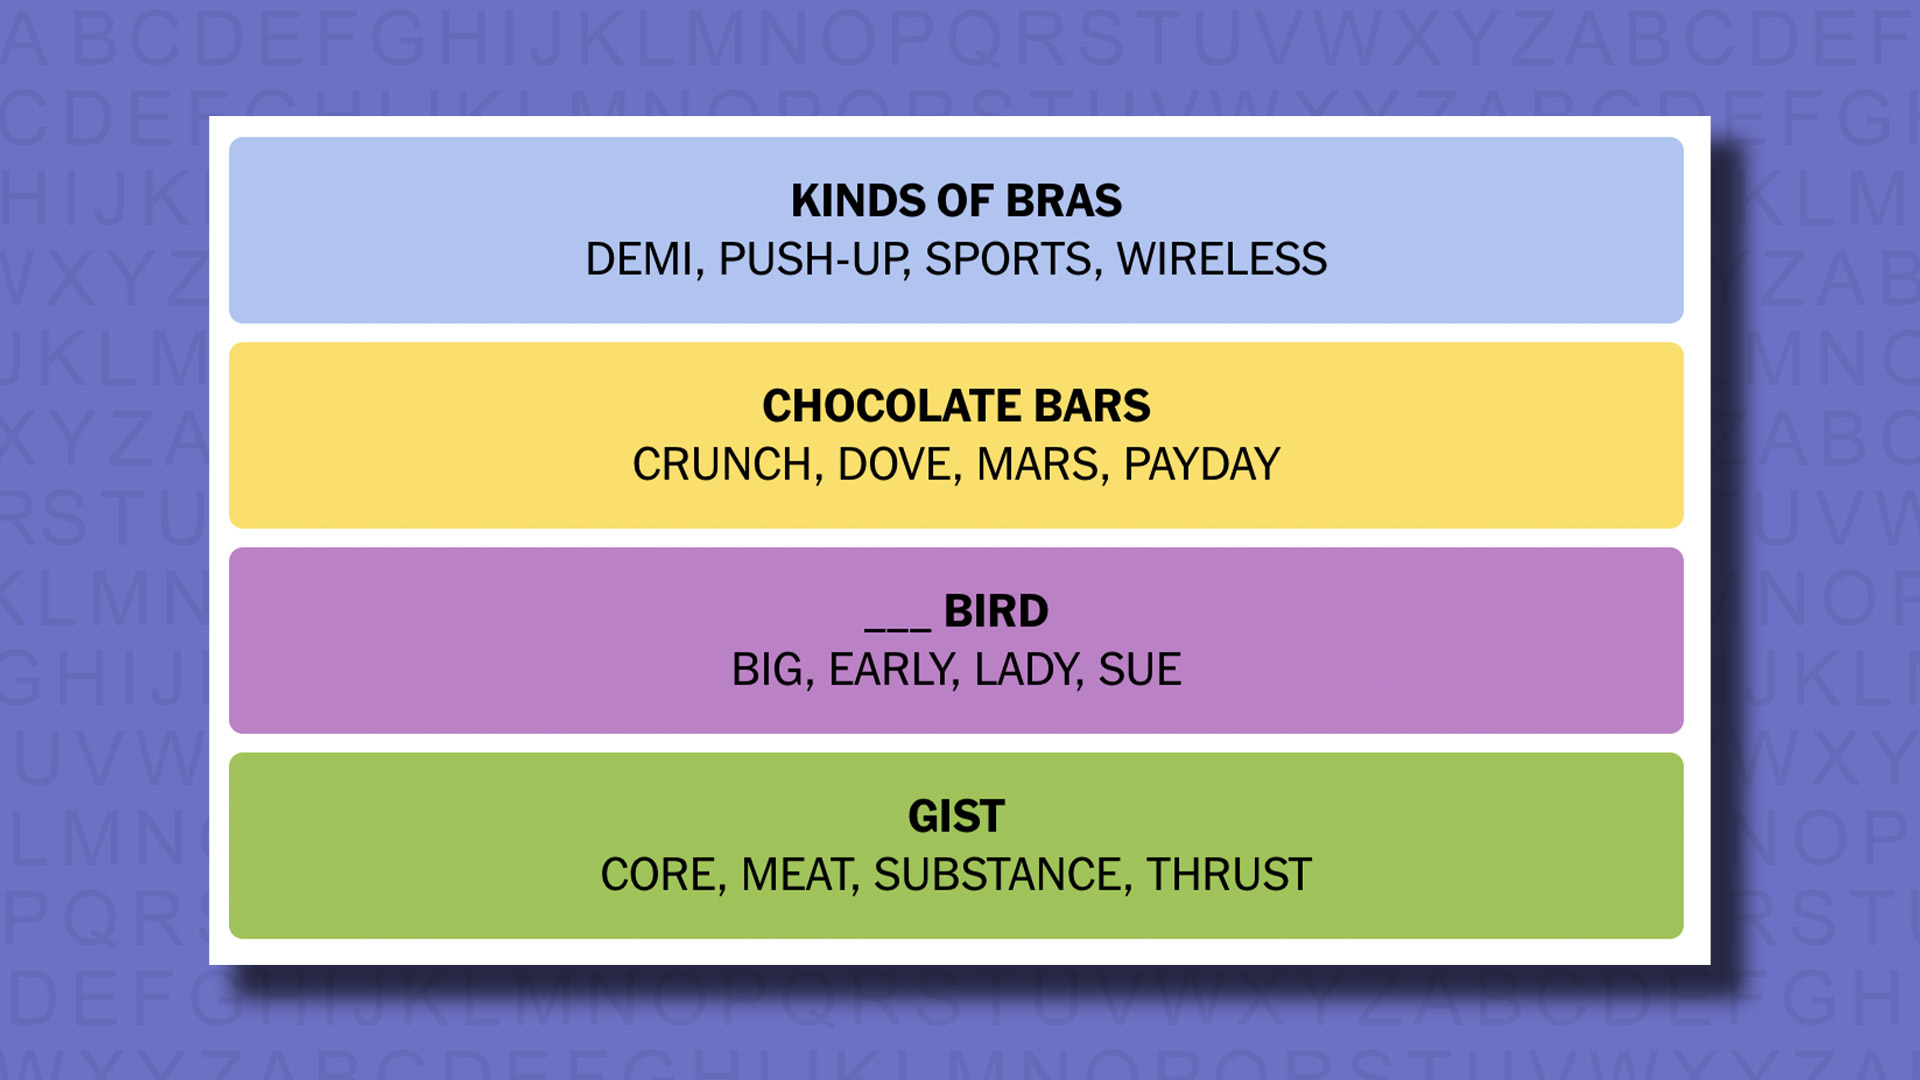
NYT Connections answers for game 519 on a purple background

(Image credit: New York Times)

The answers to today's Connections, game #519, are…

  • YELLOW: CHOCOLATE BARS CRUNCH, DOVE, MARS, PAYDAY
  • GREEN: GIST CORE, MEAT, SUBSTANCE, THRUST
  • BLUE: KINDS OF BRAS DEMI, PUSH-UP, SPORTS, WIRELESS
  • PURPLE: ___ BIRD BIG, EARLY, LADY, SUE

  • My rating: Hard
  • My score: 3 mistakes

Phew, this was a tough one! I needed all three extra guesses to solve it, and there was a large amount of guesswork involved in my answers too. I could easily have lost my streak here.

The problem was that all four groups were really tough; there appears to be no difficulty curve to it at all. Maybe yellow, supposedly the easiest of the four, is simple for some people – but not for me. I'm based in the UK, where PAYDAY, CRUNCH and DOVE are not famous CHOCOLATE BARS. Fortunately, I knew that PAYDAY and DOVE were US brands, and CRUNCH was an obvious one to go along with those two and MARS.

I also solved blue, KINDS OF BRAS, thanks to a shot-in-the-dark guess; I'm no expert (obviously), but had heard of PUSH-UP, WIRELESS and SPORTS – but not DEMI. But the latter sounded like it might fit, so in the absence of other ideas I went with it and got it right.

Purple was a monster. Eventually, I realized that LADY and BIG could both preceed BIRD, then spotted EARLY too. But I didn't have a fourth. Eventually, I guessed SUE simply because it seemed more likely than the other words I had left, MEAT, THRUST, CORE and SUBSTANCE. Apparently SUE BIRD is/was a US basketball player…

So, a very US-focused game today, and not particularly satisfying for me. But I got there in the end thanks to a lot of luck.

How did you do today? Send me an email and let me know.


Yesterday's NYT Connections answers (Sunday, 10 November, game #518)

  • YELLOW: BARREL-SHAPED CONTAINER CASK, CYLINDER, DRUM, TANK
  • GREEN: GUIDE PILOT, SHEPHERD, STEER, USHER
  • BLUE: N.F.L. TEAM MEMBER COWBOY, JET, RAM, RAVEN
  • PURPLE: THINGS THAT SWING GOLFER, PENDULUM, SALOON DOORS, SWING

What is NYT Connections?

NYT Connections is one of several increasingly popular word games made by the New York Times. It challenges you to find groups of four items that share something in common, and each group has a different difficulty level: green is easy, yellow a little harder, blue often quite tough and purple usually very difficult.

On the plus side, you don't technically need to solve the final one, as you'll be able to answer that one by a process of elimination. What's more, you can make up to four mistakes, which gives you a little bit of breathing room.

It's a little more involved than something like Wordle, however, and there are plenty of opportunities for the game to trip you up with tricks. For instance, watch out for homophones and other word games that could disguise the answers.

It's playable for free via the NYT Games site on desktop or mobile.


from TechRadar - All the latest technology news https://ift.tt/cFBI048

Arcane's showrunners have explained why a big 'CaitVi' incident was delayed until season 2 The moment felt like a better fit...


  • Arcane's showrunners have explained why a big 'CaitVi' incident was delayed until season 2
  • The moment felt like a better fit for season 2's story
  • The show's animated team couldn't have done it justice in season 1, either

Full spoilers immediately follow for Arcane season 2 episode 3.


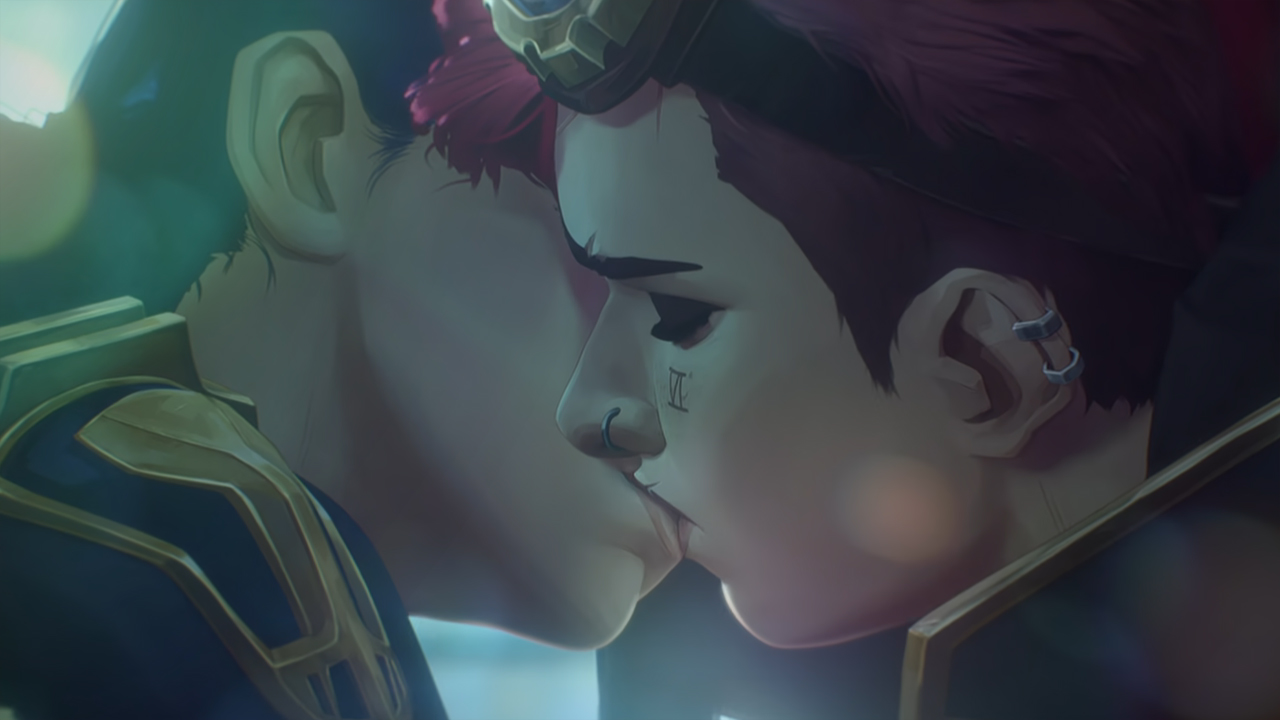
The creators of Arcane have opened up on why season 2's third episode was the perfect place to finally give fans a big moment they've waited years for: an official Caitlyn and Vi kiss.

In an exclusive chat with TechRadar, which took place before Arcane season 2 premiered on Netflix yesterday (November 9), Alex Yee and Christian Linke explained the reasons behind holding back that crowd-pleasing moment until season 2 act 1's final chapter.

The pair's smooch has, as I mentioned, been a long time coming. Ever since Caitlyn and Vi – or, as Arcane's fandom affectionately dubbed them, 'CaitVi' – met in season 1 episode 4, viewers have been convinced they have feelings for each other. There was plenty of evidence to suggest this throughout one of the best Netflix shows' first season, too, especially as the Piltovan enforcer and Zaunite brawler grew closer with each installment.

Unfortunately, due to more explosive story beats, 'CaitVi' fans were left hanging about the pair's 'will they, won't they' dynamic. Indeed, with no resolution forthcoming by the end of season 1, and its sequel season taking three years to land on the world's best streaming service, audiences have endured a long wait for this moment.

At long last, though, it's happened. This season's third episode, titled 'Finally Got The Name Right', sees the pair let their guard down and confirm their attraction to one another. And that long-awaited kiss will be celebrated by Arcane's global fanbase. Even so, why did Yee and Linke wait until this chapter to give the people what they want? Expectedly, it all boils down to the story that the pair and Arcane's wider writing team wanted to tell.

Caitlyn and Vi finally kiss in Arcane season 2 episode 3

Oh my god it's finally happening! Everyone stay calm! (Image credit: Netflix)

"They've both just lost something at the start of season 2," Linke said, alluding to the fact that Caitlyn's mom was one of the councilors revealed to have perished in Arcane season 2's premiere and that Vi's estranged sister Jinx was the culprit. "I think they're both very afraid of change, too, and they have that moment in episode 3 where they're still holding onto those things that have slipped away from them because they're starting to tread down this dark path [of seeking revenge on Jinx].

"In the wake of what Caitlyn's lost, Vi can sense there's a fragile trust in this relationship they have, and there's this moment coming up where they'll both have to decide how they're going to be when they're staring down the barrel when they find and fight Jinx. It's a fragile moment, the calm before the storm, and they're both thinking 'this may be the last moment we're going to have together.'"

I think they're both very afraid of change

Christian Linke, Arcane co-creator

"In that moment, Vi is making a big commitment to Caitlyn by choosing her over Jinx," Yee added. "And I think that's ultimately why Caitlyn takes the lead [in instigating the kiss].

"It feels wrong not to give a shout-out to [lead writer] Amanda [Overton] at this point. The relationship between Caitlyn and Vi is something that fans have carried for a very long time, and we knew it was something we wanted to bring to fruition. Amanda really championed that cause and a lot of the specific mechanics of that dynamic she had a huge part in."

'It wouldn't have been possible from a technical standpoint'

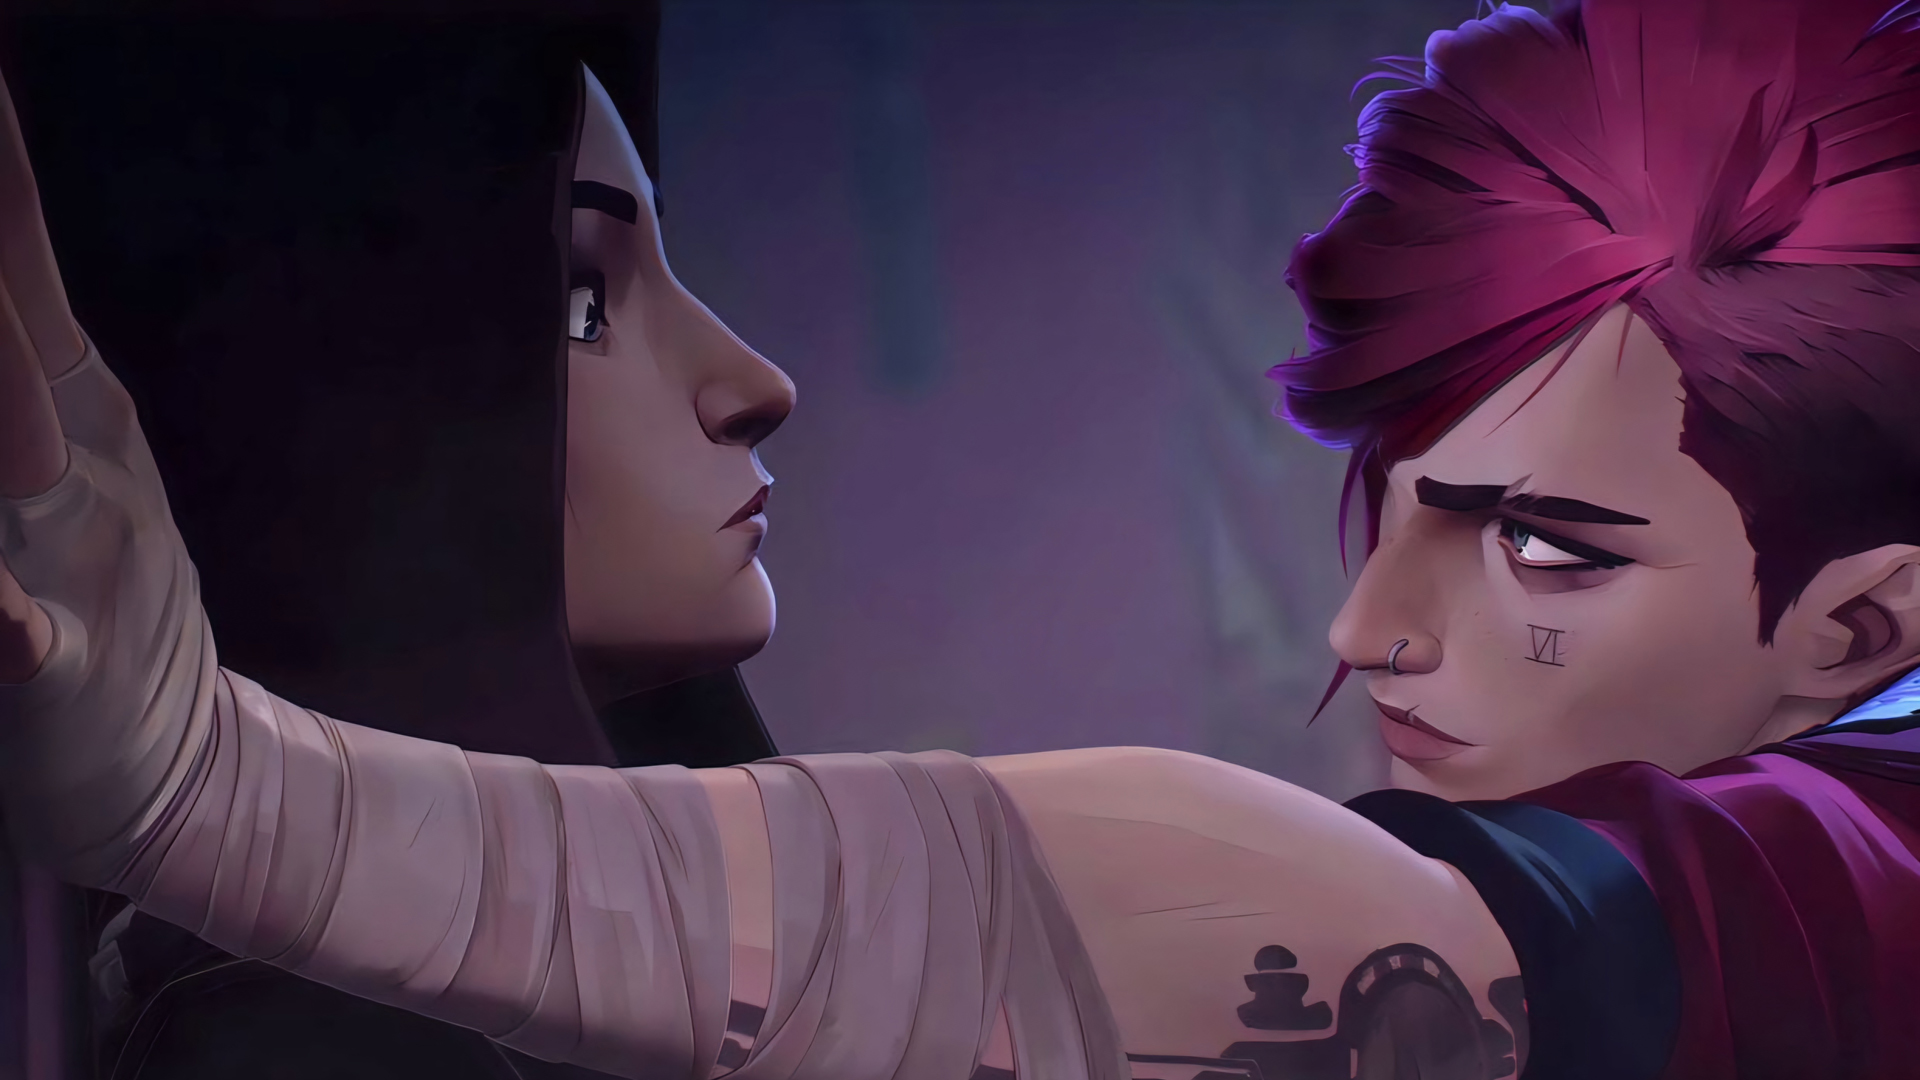
Caitlyn looking shocked as she's backed into a wall by Vi in Arcane season 1

Caitlyn and Vi could've kissed in season 1, but I'm glad they didn't (Image credit: Netflix/Riot Games/Fortiche)

The decision to delay Caitlyn and Vi's first kiss wasn't only determined by Arcane's storytellers, though. Linke also revealed that Fortiche Production, the animation studio that brought Riot Games and Netflix's first League of Legends (LoL) adaptation to life in such gorgeous detail, wasn't confident it had the talent or technology to do justice to such a beautifully delicate scene if it had been included last season.

"Interesting tidbit: I actually spoke to Bart [Barthelemy Maunoury], our animation director, about the kiss last week," Linke said. "He was asked the same question and he later told me if we'd written that last season, the animation team wouldn't have been able to do it well because they weren't technically capable yet.

"So, he thanked us for not doing that!" Linke jokingly added. "He said 'I don't think we would've done a good job. We couldn't have done it in season one', so it was interesting to hear that it wouldn't have been possible from a technical standpoint, even if we'd have wanted to do it."

I've got more to share from my exclusive chat with Yee and Linke, but you'll have to wait until season 2 act 2 arrives on November 16 to read more. In the meantime, check out more of my coverage of Arcane's second and final season below. Alternatively, read my Arcane season 2 review for more teases about its next three episodes, or my Arcane season 2 act 1 ending explained piece for answers to your biggest queries after the first three entries.

You might also like


from TechRadar - All the latest technology news https://ift.tt/oFYt42p

As the demand for cybersecurity solutions continues to rise in response to complex threats, iStorage has made a strategic move to boost th...

As the demand for cybersecurity solutions continues to rise in response to complex threats, iStorage has made a strategic move to boost the encrypted data storage landscape with the acquisition of Kanguru Solutions.

iStorage is probably best known for its PIN-authenticated, hardware-encrypted portable data storage and cloud encryption devices, and Kanguru for offering secure hardware-encrypted devices and advanced duplication and remote management capabilities.

The company says its acquisition will enable iStorage to provide a more comprehensive product lineup, offering customers greater flexibility and security when managing sensitive data across multiple devices.

Enhancing global security offerings

"This acquisition is transformative for iStorage, reinforcing our commitment to delivering ultra-secure, flexible, and affordable data management solutions," noted John Michael, Founder & CEO of iStorage.

"Joining the iStorage family allows us to expand our encryption and storage solutions to a wider audience, especially across North and South America. Together, we will drive innovation and redefine the possibilities in data protection," said Nate Cote, Managing Director of Kanguru.

You might also like


from TechRadar - All the latest technology news https://ift.tt/Vqvxko5

Arcane 's creators have explained why those councillors died in season 2 episode 1 The duo say it was "always planned that way...


  • Arcane's creators have explained why those councillors died in season 2 episode 1
  • The duo say it was "always planned that way"
  • There were never any discussions about killing off other Piltover council members

Full spoilers follow for Arcane's season 1 finale and season 2 premiere.


Arcane's showrunners have revealed how they decided who died – and who didn't – as a result of Jinx's explosive attack on Piltover's council chamber.

Speaking exclusively to TechRadar ahead of Arcane season 2 making its Netflix debut yesterday (November 9), Christian Linke and Alex Yee discussed the process of determining which characters they were going to kill off.

In the season 1 finale, titled 'The Monster You Created', Jinx used her Hextech-powered Fishbones rocket launcher to fire a missile at Piltover's council chamber. At the time, the so-called City of Progress' leaders were meeting to validate Jayce's plan to give Zaun – Piltover's deprived cousin, which deuteragonists Jinx and Vi are citizens of – its independence. In practice, that would mean Zaunites wouldn't be governed by Piltover's council anymore.

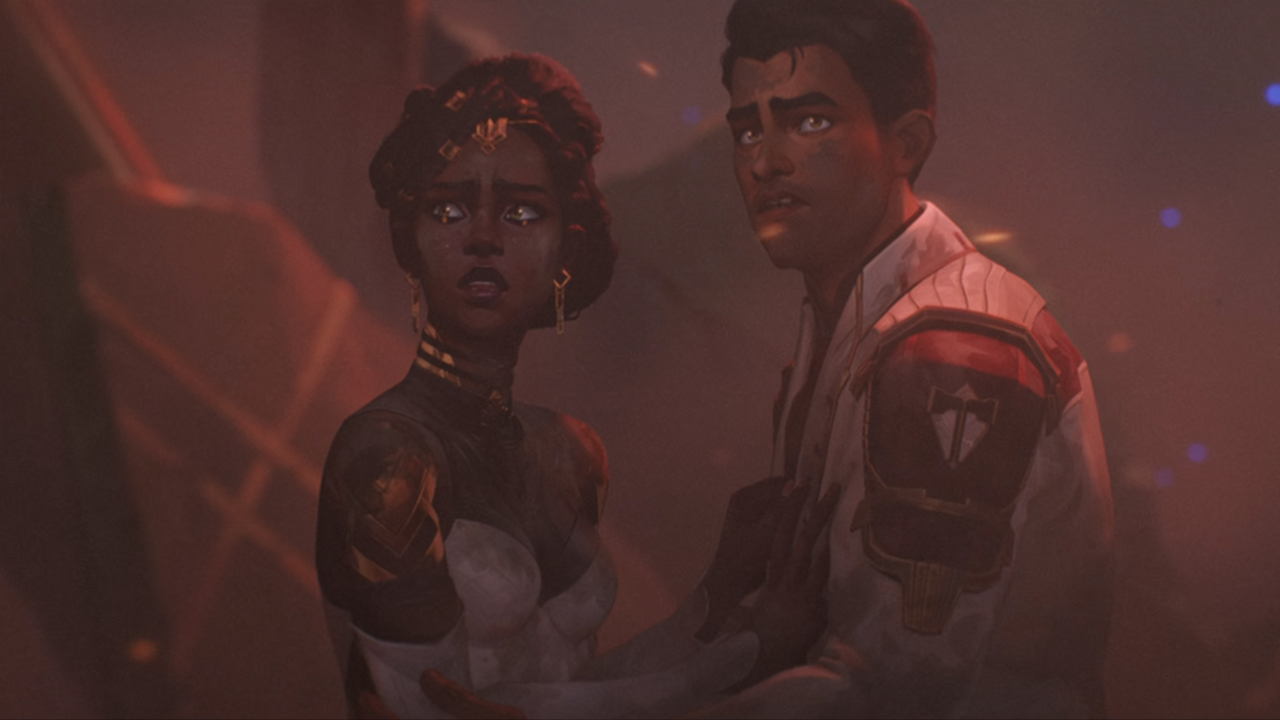
A traumatized Mel and Jayce look around Piltover's ruined council chamber in Arcane season 2 episode 1

Don't worry, Mel and Jayce survived (Image credit: Netflix)

Jinx's attack, though, ends any hopes of Zaun being an independent state. Even worse, the projectile that causes such devastation, as evidenced by season 2's opening scene, kills three Piltovan council members: Irius Bolbok, Torman Hoskel, and, most importantly, Cassandra Kiramman, Caitlyn's mom and Jayce's patron. Meanwhile, Jayce's scientific partner Viktor is severely wounded by the blast, while two other councillors – Shoola and Salo – are also injured, with Salo coming off worse out of the pair when falling masonry paralyzes him from the waist down.

With eight Piltovans, Jayce and his fellow councillor/love interest Mel included, present in the chamber during the attack, any of them could've died in the hit Netflix show's season 1 finale. Of course, thanks to some characters' established history in League of Legends, Riot Games' popular video game franchise that Arcane is based on, at the very least I expected Jayce and Viktor to survive. Indeed, I stated as much in my piece on eight huge questions that Arcane season 2 needs to answer before the animated series ends.

The aforementioned duo notwithstanding, though, how did Linke and Yee decide on who, out of the remaining six individuals, would die in one of the best Netflix shows' season 2 premiere?

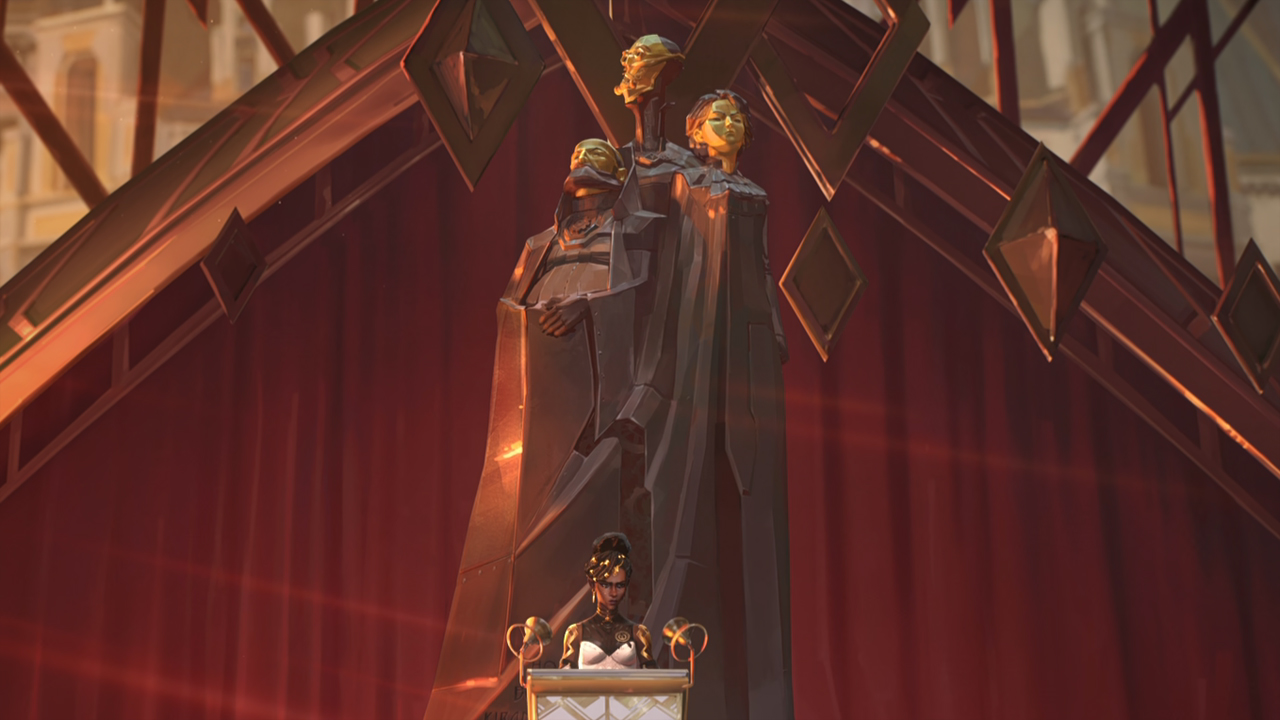
Mel delivers a speech in front of a councillor memorial monument in Arcane season 2 episode 1

Piltover's memorial to its deceased council members is unveiled later in episode 1 (Image credit: Netflix)

"I think it was always planned that way [for that trio to die]," Linke said. "It [Jinx's attack] was supposed to bring out Mel's abilities [to shield those in close proximity to her], and it also forced Jayce's hand with what happens with Viktor and how Jayce uses the Hexcore to save his life."

"Hoskel and Bolbok, though..." Yee interjected, before he jokingly added: "There are some big fans on the team for those counselors!"

Speaking of things that were planned – or, in this case, weren't planned – Linke and Yee also told me that it was "never the plan" for Arcane to run for five seasons on the world's best streaming service. Even if it had, though, I'm convinced that there would be enough plot armor to protect Jayce and Viktor for many more episodes to come. Still, let's all pour one out for Cassandra. I guess we should do likewise for Hoskel and Bolbok, too, even though they continually riled up viewers with their decision-making in season 1.

Anyway, you can expect more exclusives from my chat with Linke and Yee in the days and weeks ahead. For now, read my Arcane season 2 review for more details about the next three episodes, plus my Arcane season 2 act 1 ending explained piece for answers to your biggest questions after its first three chapters.

You might also like


from TechRadar - All the latest technology news https://ift.tt/r6tIzxq

It was my birthday a few weeks ago, and as if that didn’t make me feel old enough, the Firefox browser has just turned exactly 20 years ol...

It was my birthday a few weeks ago, and as if that didn’t make me feel old enough, the Firefox browser has just turned exactly 20 years old today. Yes, Firefox version 1.0 launched on November 9, 2004 – and I've been using it for almost as long as it's been alive, picking it up in the mid-noughties and loading it onto every computer I’ve used in the years since.

Over all that time, I’ve stuck with Firefox through thick and thin (and Chrome's increasing dominance). It’s clear to me that Firefox has always done a few things far better than rivals like Chrome and Safari – things that those web browsers are unlikely to ever match.

Right from when I started using Firefox, what drew me to it was its strong stance on privacy. It’s always been important to me that my data stays my own and is not sold to anyone else for profit. It’s not always possible to stop that happening, but with Firefox, it’s a whole lot easier.

That’s because Firefox blocks all sorts of trackers that can invade your privacy and follow you around the web. Cookies are isolated to stop them building a detailed picture of you, and Firefox limits access to data that can be used to create a digital “fingerprint” of your browsing habits by less conscientious websites and services.

That’s just scratching the surface of its privacy-protecting features, and I’m still glad to have them at my disposal whenever I use the web.

Chrome’s privacy problem

A graphical rendering of the Mozilla Firefox web browser.

(Image credit: Growtika / Unsplash)

Take a look at Google Chrome and the contrast is stark. Chrome doesn’t block trackers by default, nor does it offer fingerprint blocking. It monitors the websites you visit and uses this data to send you targeted ads. While you can block some of the topics it identifies, you can’t stop it finding other ad topics to share with websites. It’s going to sell your private data, whether you want it to or not.

While Google has considered implementing pro-privacy features, it’s often backtracked when it became apparent how much that could impact third-party advertisers and data brokers. Just look at the Privacy Sandbox, which Google has watered down significantly, or the way Google often uses so-called dark patterns to lure you into sharing as much of your data as possible.

Ultimately, we shouldn’t be surprised at Chrome’s behavior. Google runs the world’s largest advertising network and has a built-in incentive to violate your privacy (and limit what you can do to stop it). Google’s privacy efforts will always be half-hearted as long as implementing policies that keep your info safe hurt its bottom line. Money talks, after all.

Things are different for Firefox because it’s developed by Mozilla, a group that puts privacy at the forefront of its work. Firefox is open source, too, so you know exactly what you’re getting without having to worry about hidden nasties making it into your browsing experience. In other words, it’s the antithesis of Chrome.

Actions speak louder than words, and Mozilla doesn’t just talk the talk – it follows through on what it promises, even when its features might hurt its ability to make money from its users.

In contrast, it’s clear that this is absolutely not the case with Chrome, and nor will it ever be. I know which browser I’d rather trust.

Why don’t I just use Safari?

In this photo illustration, the Mozilla Firefox logo is seen displayed on an Android mobile phone.

(Image credit: Photo Illustration by Omar Marques/SOPA Images/LightRocket via Getty Images)

If privacy is a priority for me, why haven’t I switched to Apple’s Safari browser? There’s an argument for me doing so: like Mozilla, Apple is well-known for its pro-privacy stances. Safari is generally faster than Firefox, too, helping it offer the best of both Firefox and Chrome.

But there’s a problem: Safari is limited to Apple’s own devices. I use both Windows and macOS in my day-to-day life, so I need something that will function on every device I own. Safari can’t do that, and given how disappointing Safari for Windows was back when it existed, I doubt Apple is too fussed about expanding the browser beyond its own products.

In contrast, I can get Firefox on any of my devices and it will be set up just as I expect it to be, with all the extensions, bookmarks and tabs right where they should be. I can send a tab from Firefox on my Windows PC to Firefox on my Mac or on my iPhone and it’ll arrive instantly, letting me pick up where I left off whatever device I’m using.

It’s that combination of cross-platform compatibility and rock-solid privacy credentials that have me still using Firefox 20 years later.

Throw in a huge library of excellent extensions and I get everything I need from Mozilla’s browser – there’s no alternative that quite matches what it can do. With 20 years in the bag, I imagine I’ll still be using Firefox in another two decades’ time.

You might also like


from TechRadar - All the latest technology news https://ift.tt/VuTJZdD

Github repositories are being infected with malware Trusted repositories can bypass secure web gateways Github comments are also being u...

  • Github repositories are being infected with malware
  • Trusted repositories can bypass secure web gateways
  • Github comments are also being used to hide malicious files

In a new phishing campaign detected by Cofense Intelligence, threat actors used a novel approach by leveraging trusted GitHub repositories to deliver malware. The campaign is aimed at exploiting the inherent trust many organizations place in GitHub as a developer platform.

Instead of creating malicious repositories, attackers chose to embed malware into legitimate ones affiliated with tax organizations such as UsTaxes, HMRC, and Inland Revenue.

This allowed them to bypass Secure Email Gateway (SEG) protections, posing a significant challenge to cybersecurity defenses. The attack also capitalized on the sense of urgency tied to filing taxes after the April deadline in the US.

Phishing tactic – abuse of trusted repositories

Emails associated with the campaign contained links to archives hosted on GitHub. Unlike traditional phishing attacks that rely on suspicious links or attachments, these emails appeared credible because the GitHub repositories used were legitimate and well-known, and can circumvent Secure Web Gateways.

The archive files linked in the emails were password protected, a tactic used to add an air of legitimacy. This protection also made it more difficult for malware scanners to detect and inspect the contents of the archive. Once opened, the password-protected files installed Remcos Remote Access Trojan (RAT) on the victim’s system, granting attackers remote control over the infected device.

A key component of this campaign was the use of GitHub comments to upload malicious files. GitHub comments are typically used by developers to communicate about a repository’s content, propose changes, or document issues. However, attackers exploited this feature by uploading malware-laden files within comments rather than the repository’s source code, allowing them to circumvent the usual security protocols and ensure that the malware remained hidden.

Even if the original comment containing the malware link was deleted, the malware itself remained accessible through the repository’s file directory. This method has been used before, most notably with the Redline Stealer malware, but this campaign represents a significant escalation in the use of GitHub comments as a malware distribution vector.

The campaign primarily targeted the financial and insurance industries, with both sectors being particularly vulnerable during tax season, as they handle a large volume of sensitive financial data.

The attackers appear to have been testing the waters with a smaller campaign, focusing on these two industries. Previous phishing campaigns using techniques like QR codes had broader targets, but the narrower focus of this attack suggests the threat actors were experimenting with the GitHub-based method before scaling up.

Phishing campaigns remain one of the most persistent and effective tactics used by cybercriminals to gain unauthorized access to sensitive information.

These attacks typically involve deceptive emails or messages that trick users into clicking malicious links, downloading harmful attachments, or revealing personal details.

Over the years, phishing techniques have evolved, becoming more sophisticated and harder to detect. Cybercriminals now leverage trusted platforms, disguise malicious intent behind legitimate-looking messages, and use advanced social engineering techniques.

You might also like


from TechRadar - All the latest technology news https://ift.tt/mCNhWOI

Welcome to another quick hit of tech news courtesy of TechRadar's ICYMI, the column that condenses all of the week's big stories in...

Welcome to another quick hit of tech news courtesy of TechRadar's ICYMI, the column that condenses all of the week's big stories into one handy list so you can catch up on what you might have missed.

What do we have in store for you this week? Well, the task of getting our PlayStation 5 Pro, MacBook M4 and Kindle Colorsoft reviews in front of you dominated our time, and you can see what we thought of them all below, but they were far from the only interesting tech stories. There were also new product releases, some beta software tests and a couple of very tasty leaks to stay on top of, so read on and find out what happened.

7. DJI unveiled its cheapest-ever FPV goggles

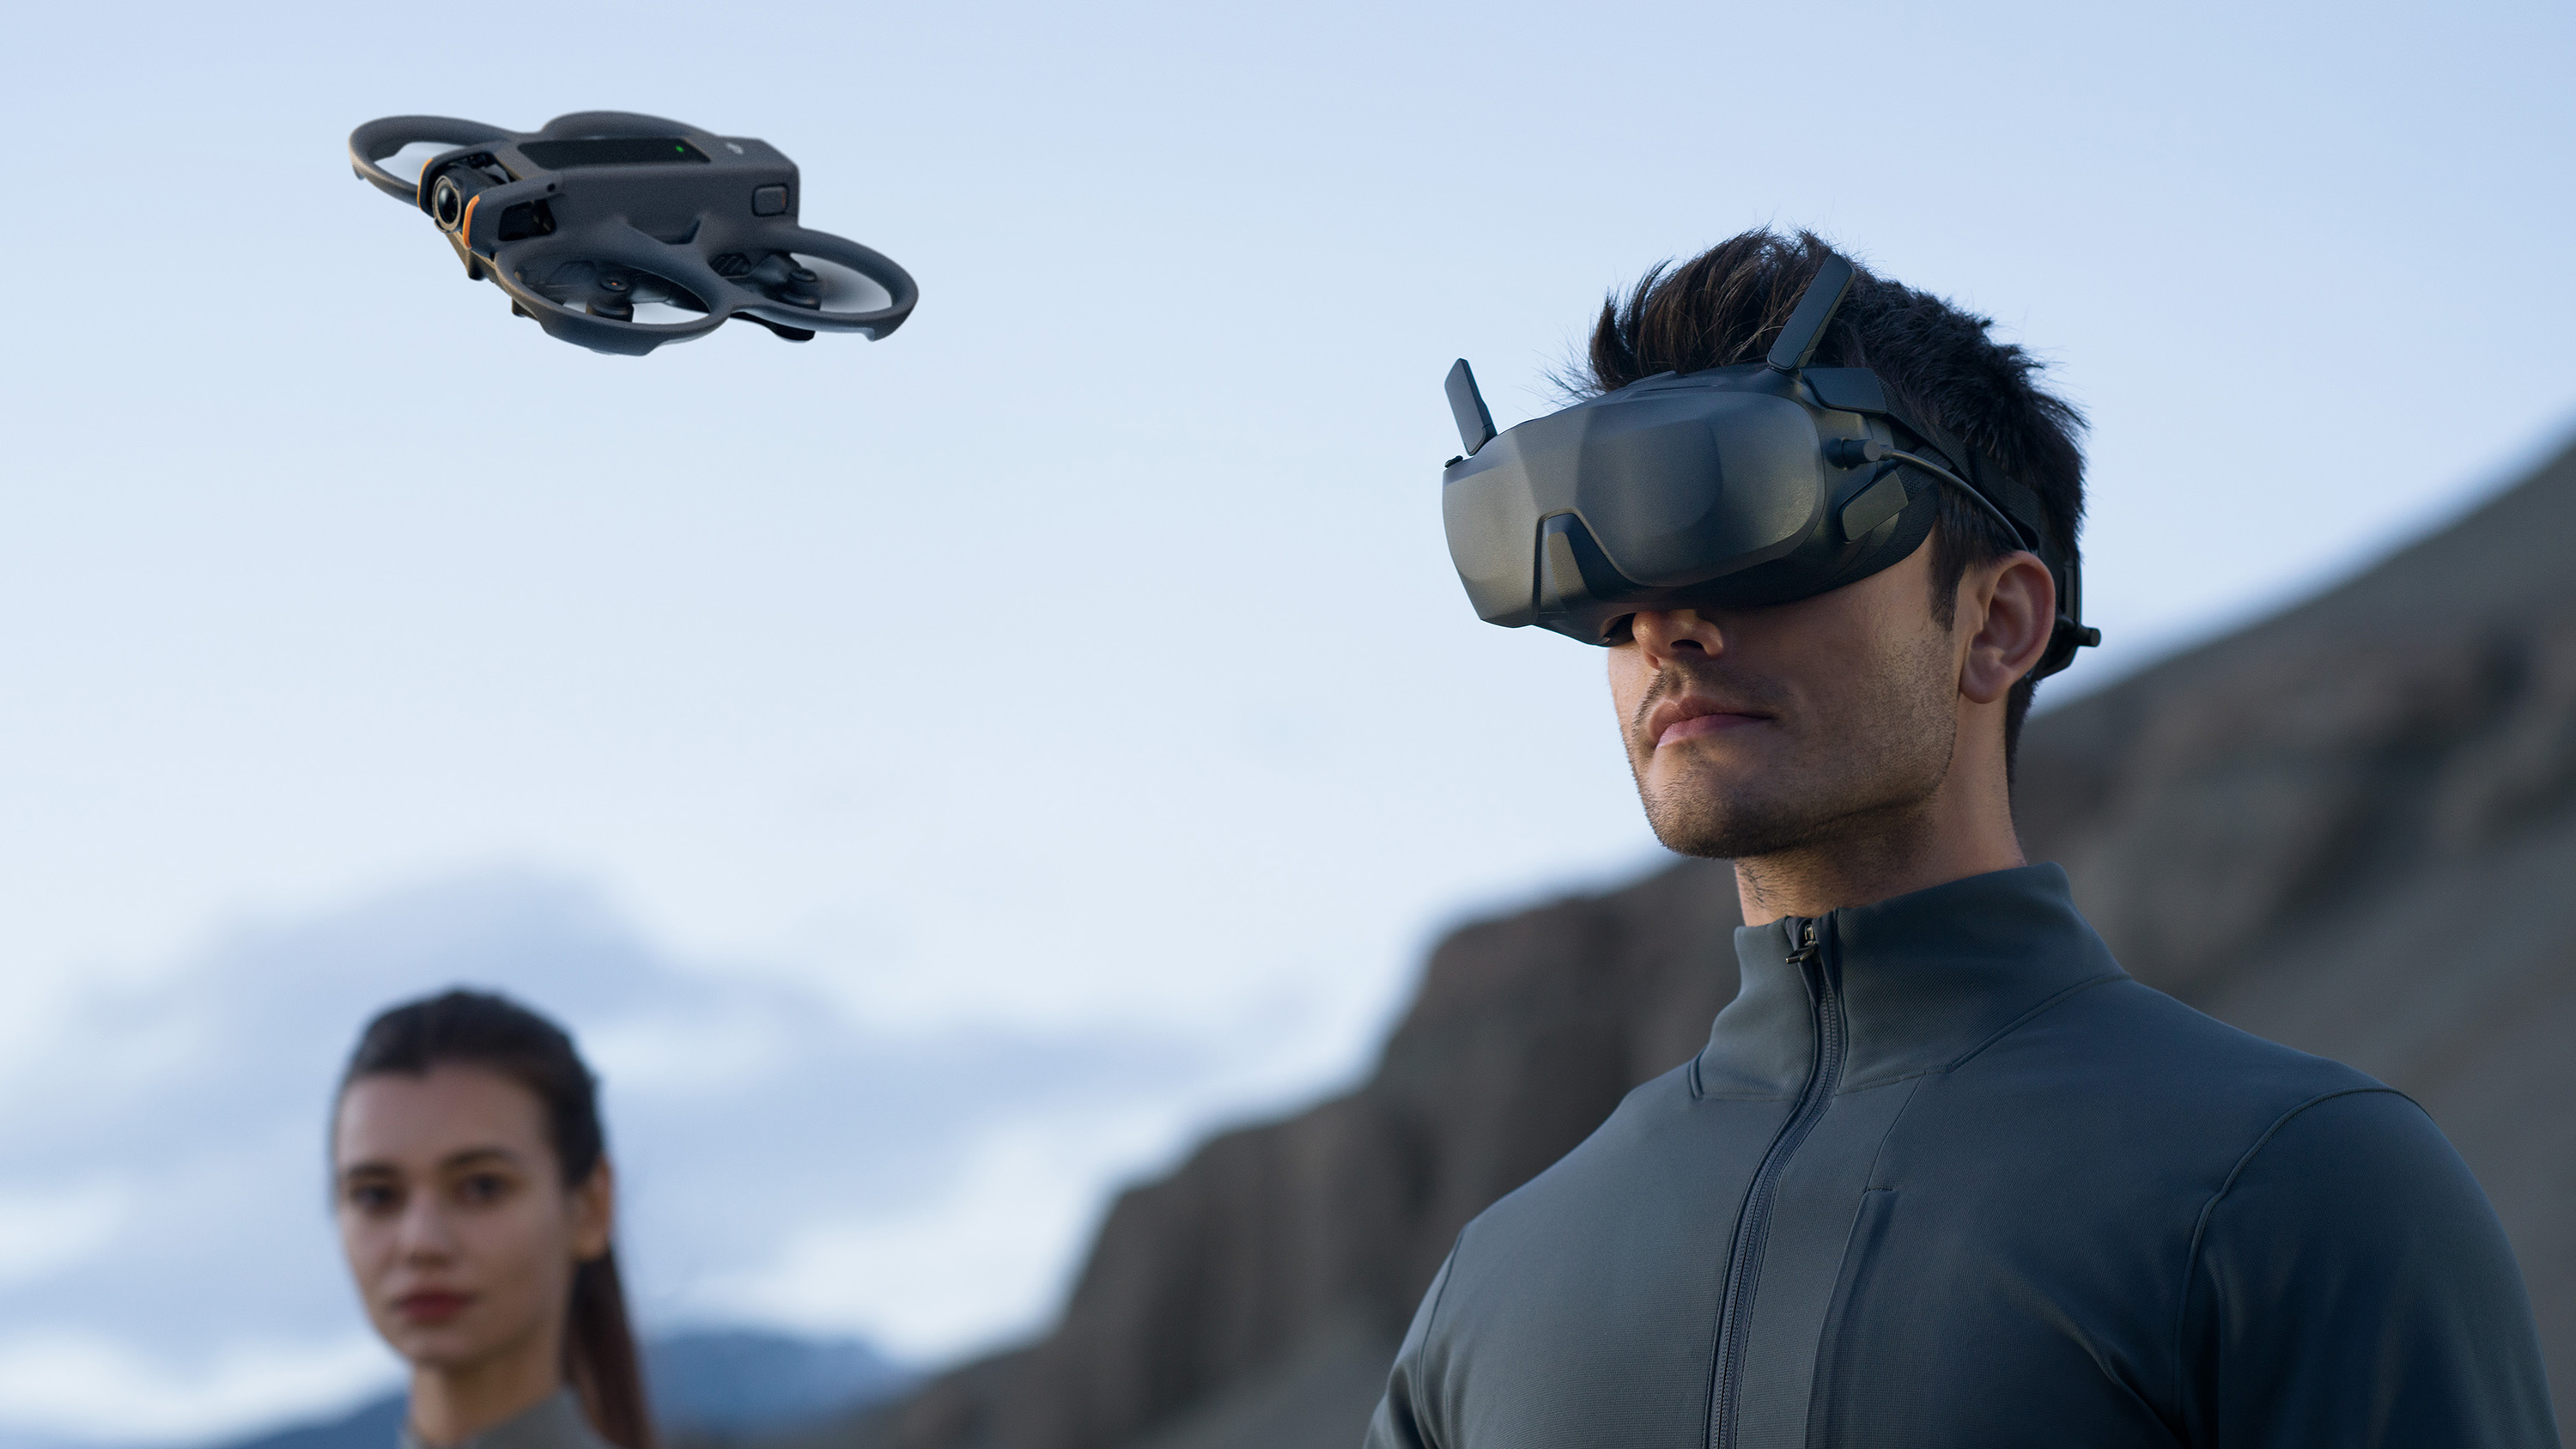
Person wearing DJI Goggles N3 with mountainous backdrop

(Image credit: DJI)

DJI unveiled the Goggles N3, its cheapest-ever FPV (First Person View) goggles for immersive drone flight. At less than half the price of the Goggles 3, they look like an excellent pairing with the Neo, DJI's cheapest-ever 4K drone with multiple flight control options, including FPV.

In fact, DJI has made a new DJI Neo Motion Fly More Combo, which includes the Goggles N3 plus additional batteries and charging hub, all for less than the pricier Goggles 3 alone.

Low price doesn't mean low quality, either – the Goggles N3 pack a crisp 1080p screen with an immersive 54-degree field of view, and can perform aerial acrobatics such as flips and rolls with a tilt of your head. They also boast DJI's latest O4 transmission, negligible 31ms latency and neat augmented reality features. At half the price of the Avata 2 with goggles, this new pairing opens up the adrenaline-fuelled world of FPV flight to a whole new audience.

6. iOS 18.2 beta showed us major Apple Intelligence upgrades

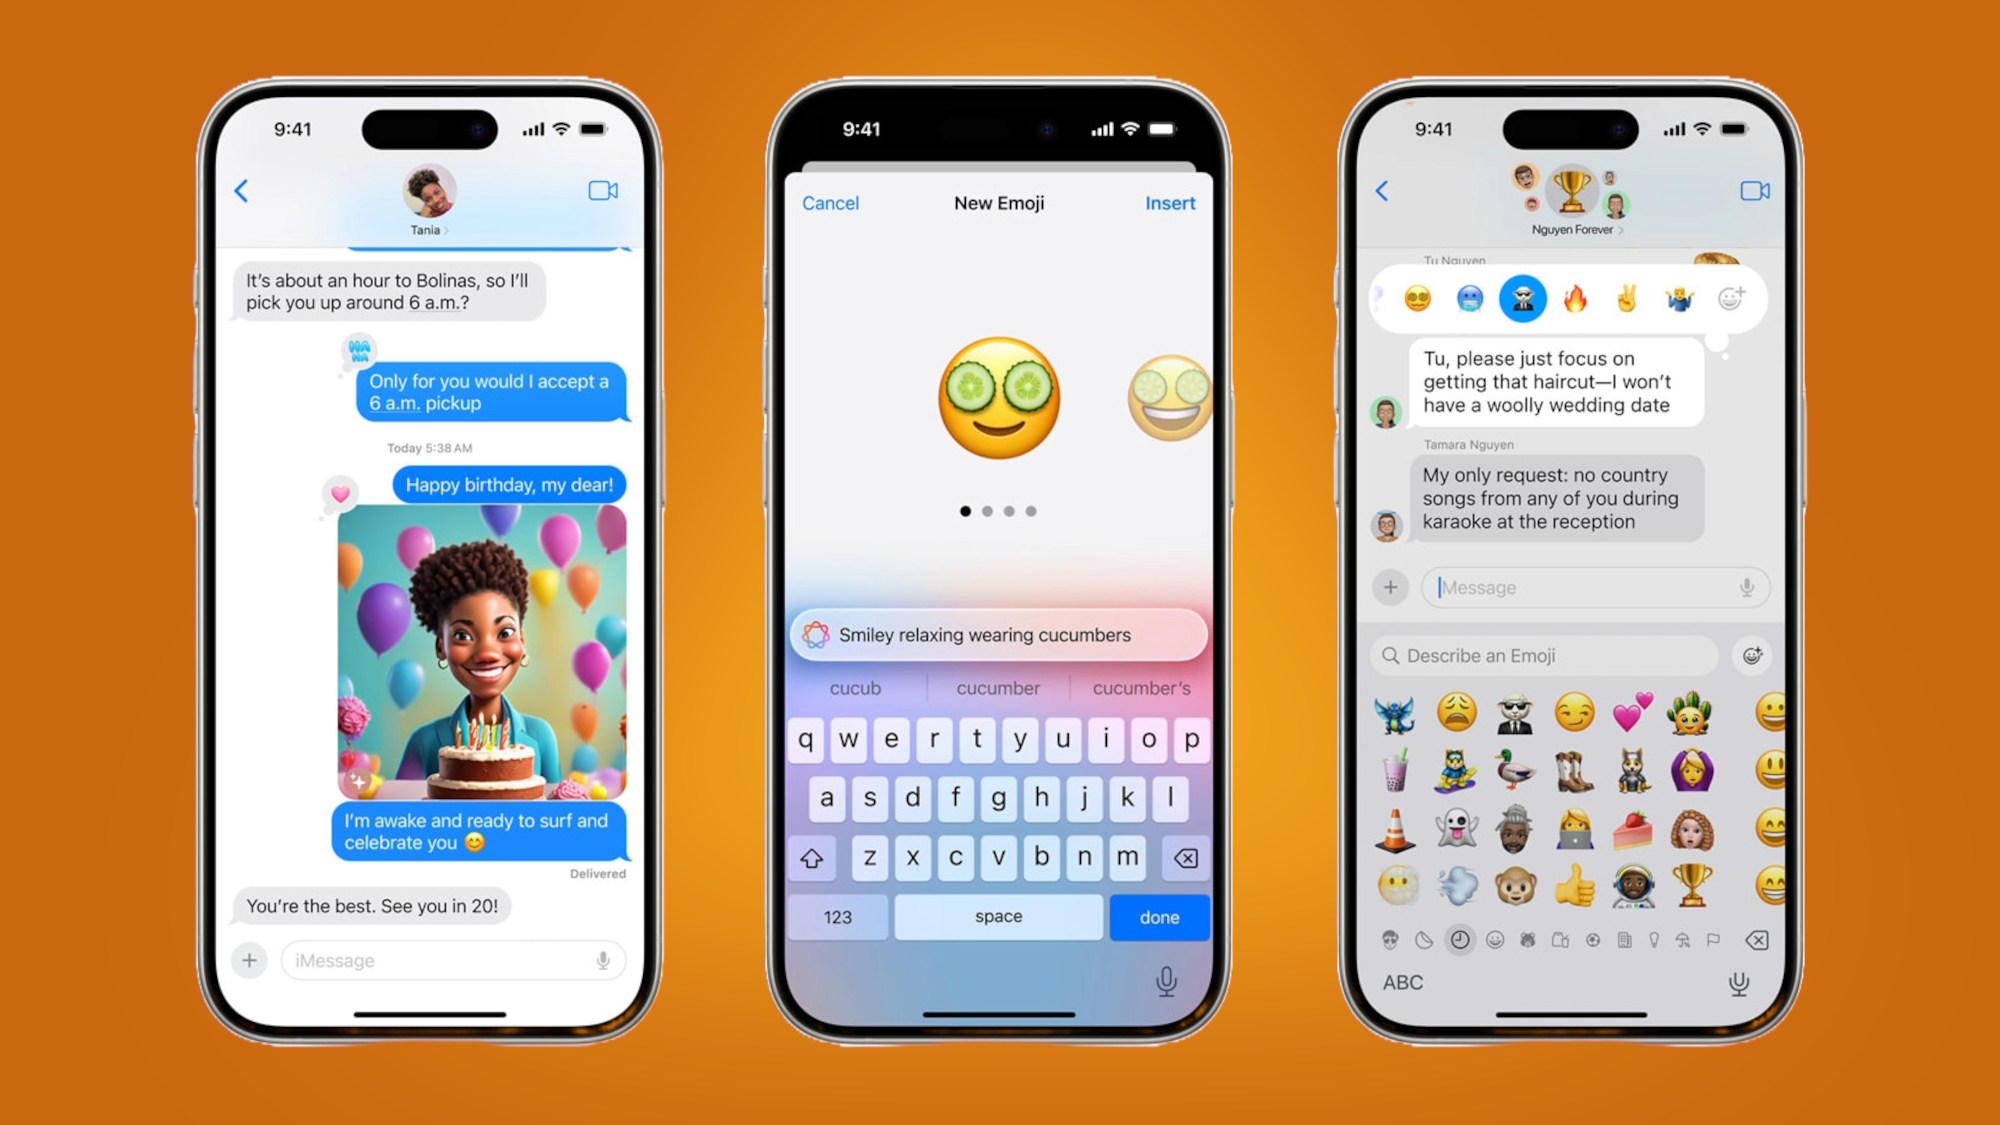
Genmoji and Image Playground in Apple Intelligence

(Image credit: Apple / Future)

Apple Intelligence landed with iOS 18.1 but it isn’t quite as spectacular as everyone hoped it would be, largely because some of its most exciting features are currently unavailable. That could change soon, though, and the iOS 18.2 update beta has given us a taste of these missing features.

Genmoji is arguably the big one here. This allows users to create a custom emoji and we’ve already fallen in love with it, declaring it "the kind of feature that will instantly impact society and our online lives." That aside, the iOS 18.2 beta also includes ChatGPT being baked into Siri (though it’ll have restrictions for free users), and the arrival of Image Playground, which offers a more standard alternative to the best AI image generators than Genmoji does.

Beyond AI, 18.2 will bring new camera control tools, easier sharing of lost item information through the Find My service, and the first hints of Siri getting abilities to understand what’s on screen.

5. A leaked benchmark got us excited about the Samsung S25 Ultra

The back of the Samsung Galaxy S24 Ultra

(Image credit: Future)

Apple has long maintained bragging rights over Samsung when it comes to the sheer under-the-hood power of its smartphones, but 2025 could see a momentum shift in favor of the Android manufacturer.

According to a new report, the Samsung Galaxy S25 Ultra could be even more powerful than the iPhone 16 Pro Max, with the upcoming Android flagship having performed exceptionally well in early benchmark tests.

We’re all but certain that the Galaxy S25 Ultra will use Qualcomm’s new Snapdragon 8 Elite chipset under the hood, and given that the likes of Xiaomi, OnePlus, and Honor have already confirmed that their respective flagships will use the same platform, the future looks extremely bright for Android fans.

4. Google leaked its Jarvis AI

Google AI

(Image credit: Shutterstock)

Oh dear! Jarvis, Google’s rumored AI agent that searches Chrome on your behalf, was accidentally leaked by the company itself earlier this week, popping up briefly in Chrome’s extension store before being swiftly removed.

While it didn't stick around for long, it gave us proof that this automated web browser – which Google describes as “a helpful companion that surfs the web with you” – is a real thing. The AI agent is expected to launch in December and will seemingly be able to surf the web, buy products, and even book flights on your behalf.

We're expecting plenty of these agents to spring up over the next few months, as companies try to innovate in the AI space; Anthropic has already released an automated agent to developers, and there also rumors that OpenAI could enter the mix, although we don’t have any information on what a ChatGPT AI agent could look like.

When will Jarvis appear for real? That's unclear, but if you’re excited at the prospect of AI doing mundane web browsing on your behalf, you might not have long to wait.

3. Amazon’s color Kindle got off to a rough start

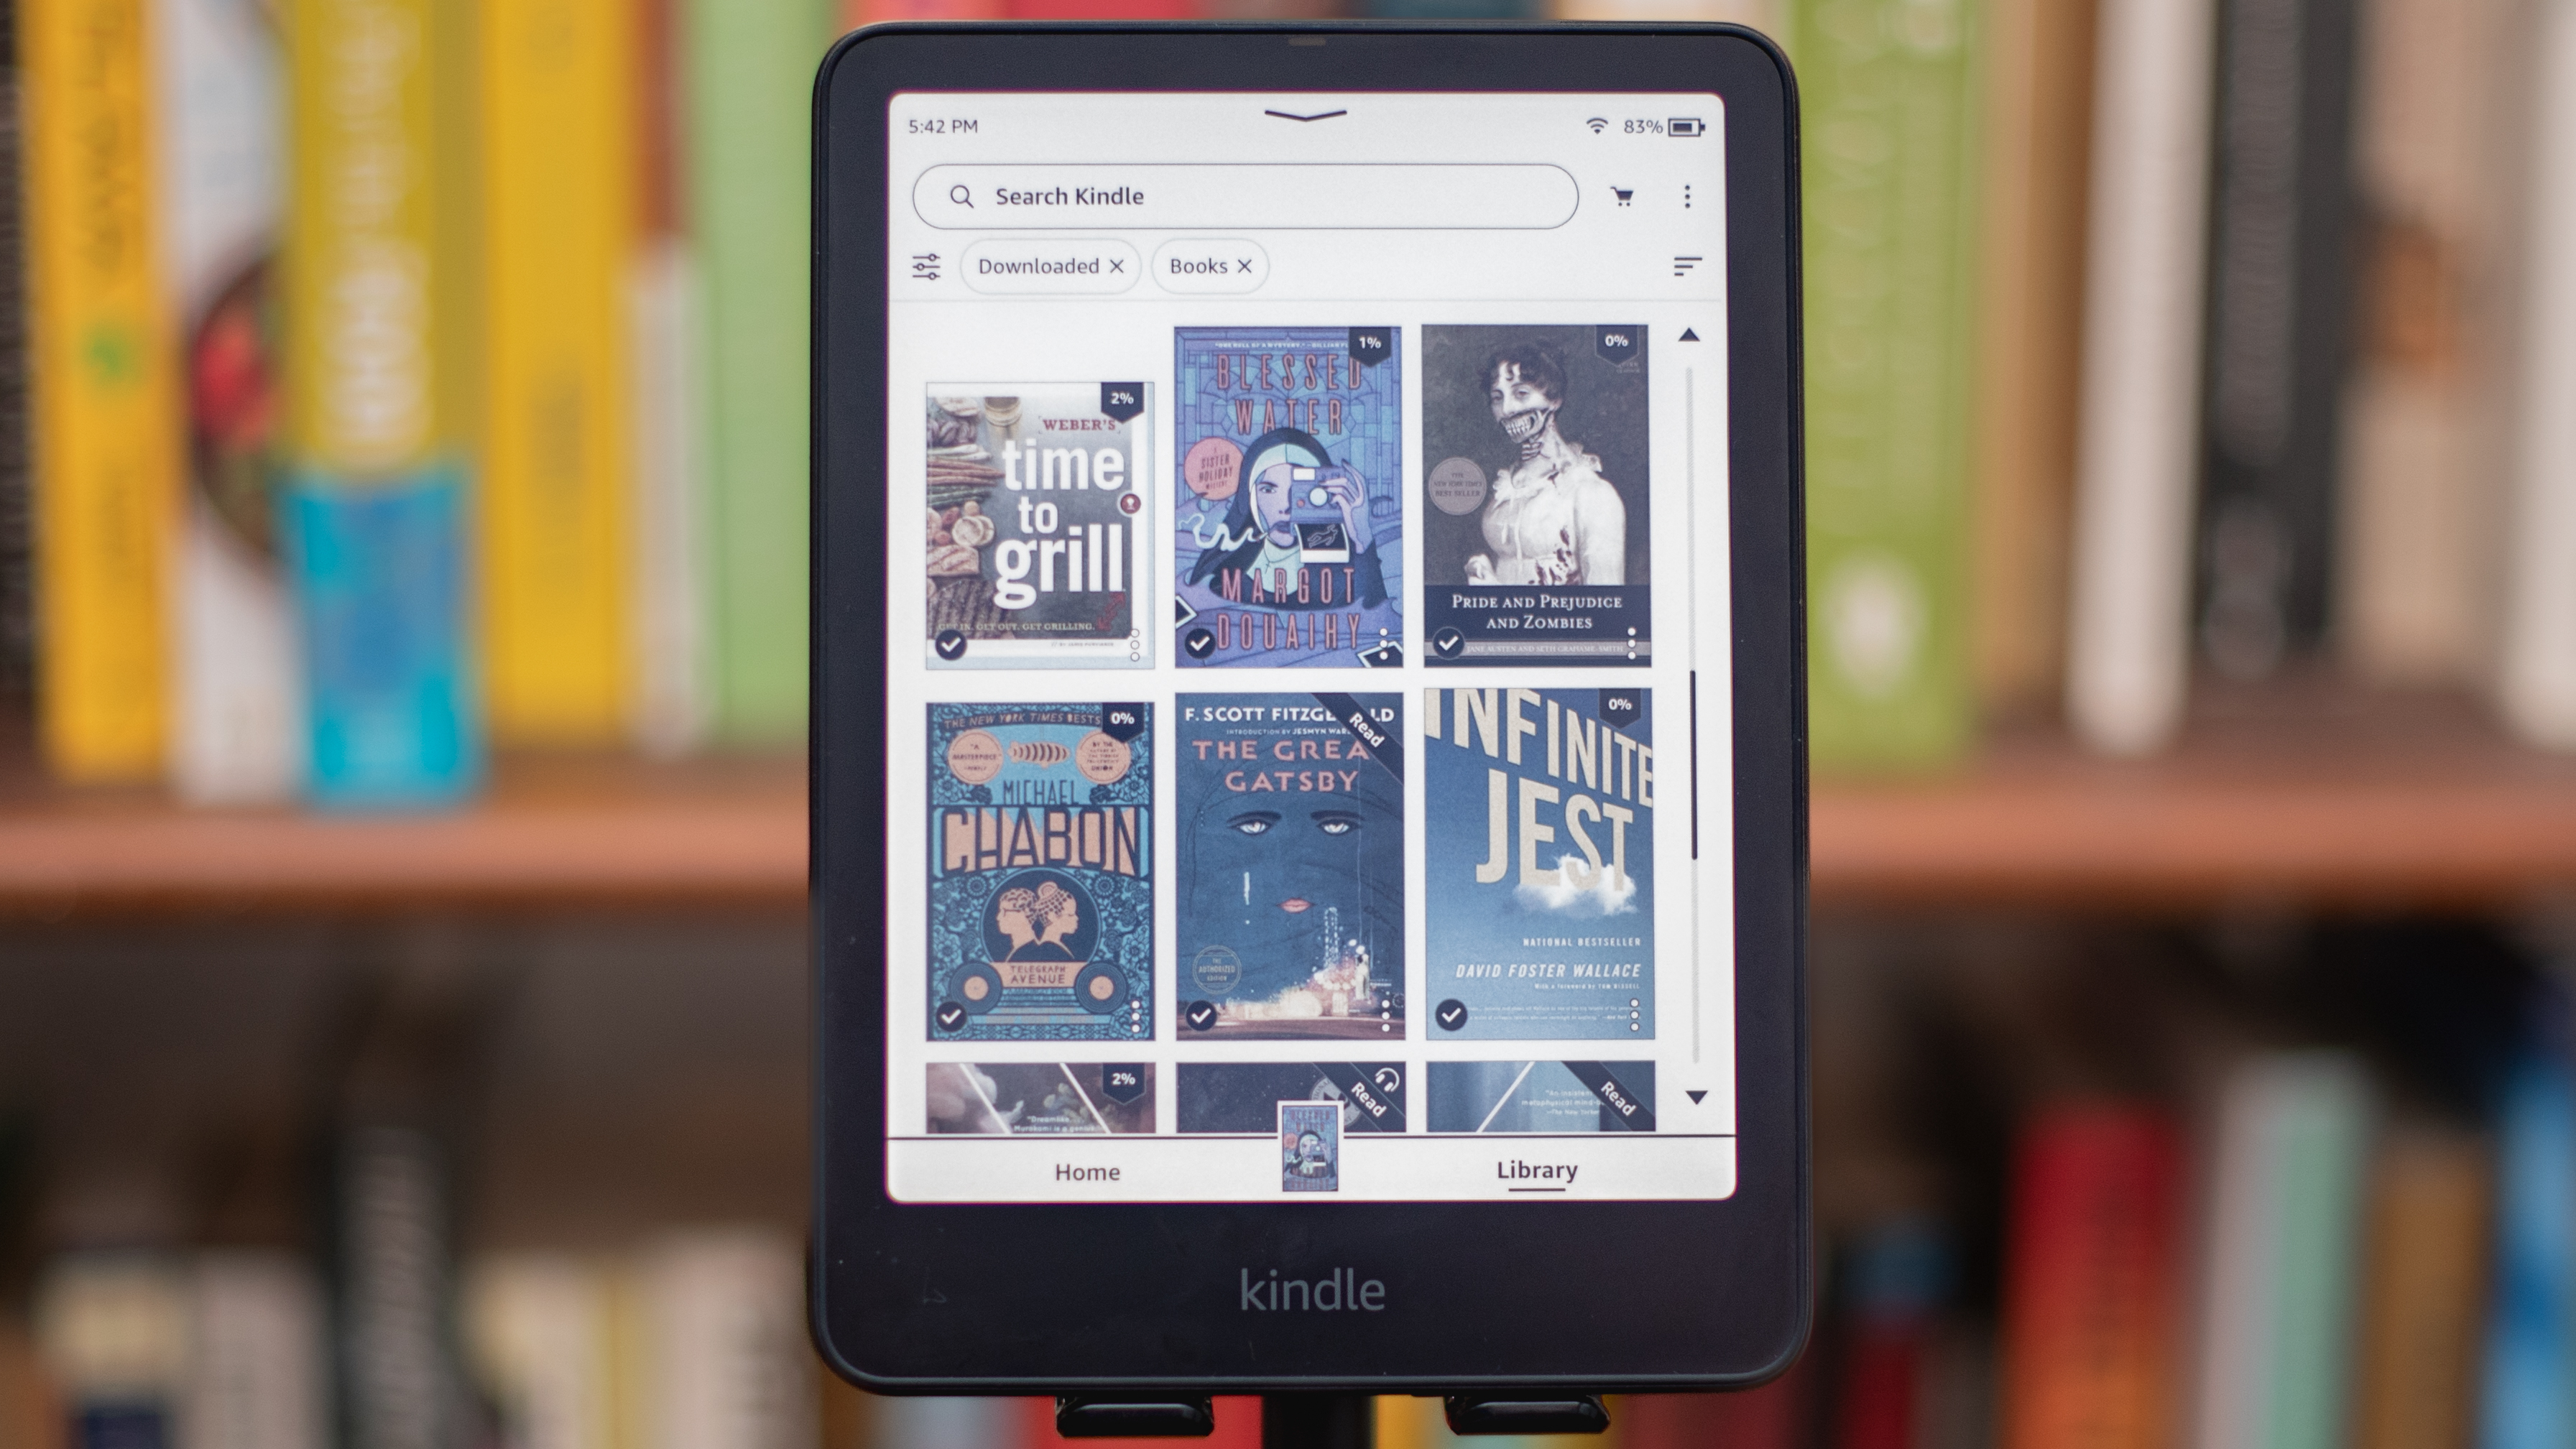
Amazon Kindle Colorsoft Signature edition e-reader showing graphic novels, cookbooks, and fiction, as well as settings

(Image credit: Philip Berne / Future)

We got our hands on the Kindle Colorsoft – awarding it four-and-a-half stars in our review – but we and others noticed that over time it started to develop a frustrating yellow tint at the bottom of its display.

Not every Colorsoft seems to be affected, and in our case the yellowing was not very noticeable, but that hasn’t prevented the store page from being flooded with negative reviews – with Amazon even calling those negative reviewers to learn more about the discoloration problem.

Amazon is still trying to implement whatever hardware or software fix it needs to, but if you already have a yellowed Colorsoft, the company has said it will offer you a refund or a replacement device.

2. We tested the PS5 Pro…

PS5 Pro

(Image credit: Sony)

The PS5 Pro is finally here and the good news is that it’s a fantastic console that offers an excellent gaming experience. It also introduces the wizardry of PSSR (that's Playstation Spectral Super Resolution, for the uninitiated). However, its price tag and lack of included disc drive really are hefty stings in its tail.

The graphical advancements offered by the PS5 Pro beautifully blend super-high levels of fidelity with fluid and smooth frame rates at the same time, and from our testing, can tangibly elevate the experience of playing games. The extra spec uplifts – such as Wi-Fi 7, an extra 2TB of storage, as well as boosts to non-enhanced PS5 and PS4 games – help to round out a premium package for those who want to be at the bleeding edge of console tech and desire the most performant console going.

All of which is great, but it’s nonetheless a bit of a hard sell for current PS5 users or anyone who's not, y'know, rich, because the advancements here are not truly transformational. Still, if you’re a PlayStation enthusiast and always want to get the most out of both performance and graphics then you'll love it.

1. …and we reviewed – and loved – the new M4 Macs, too

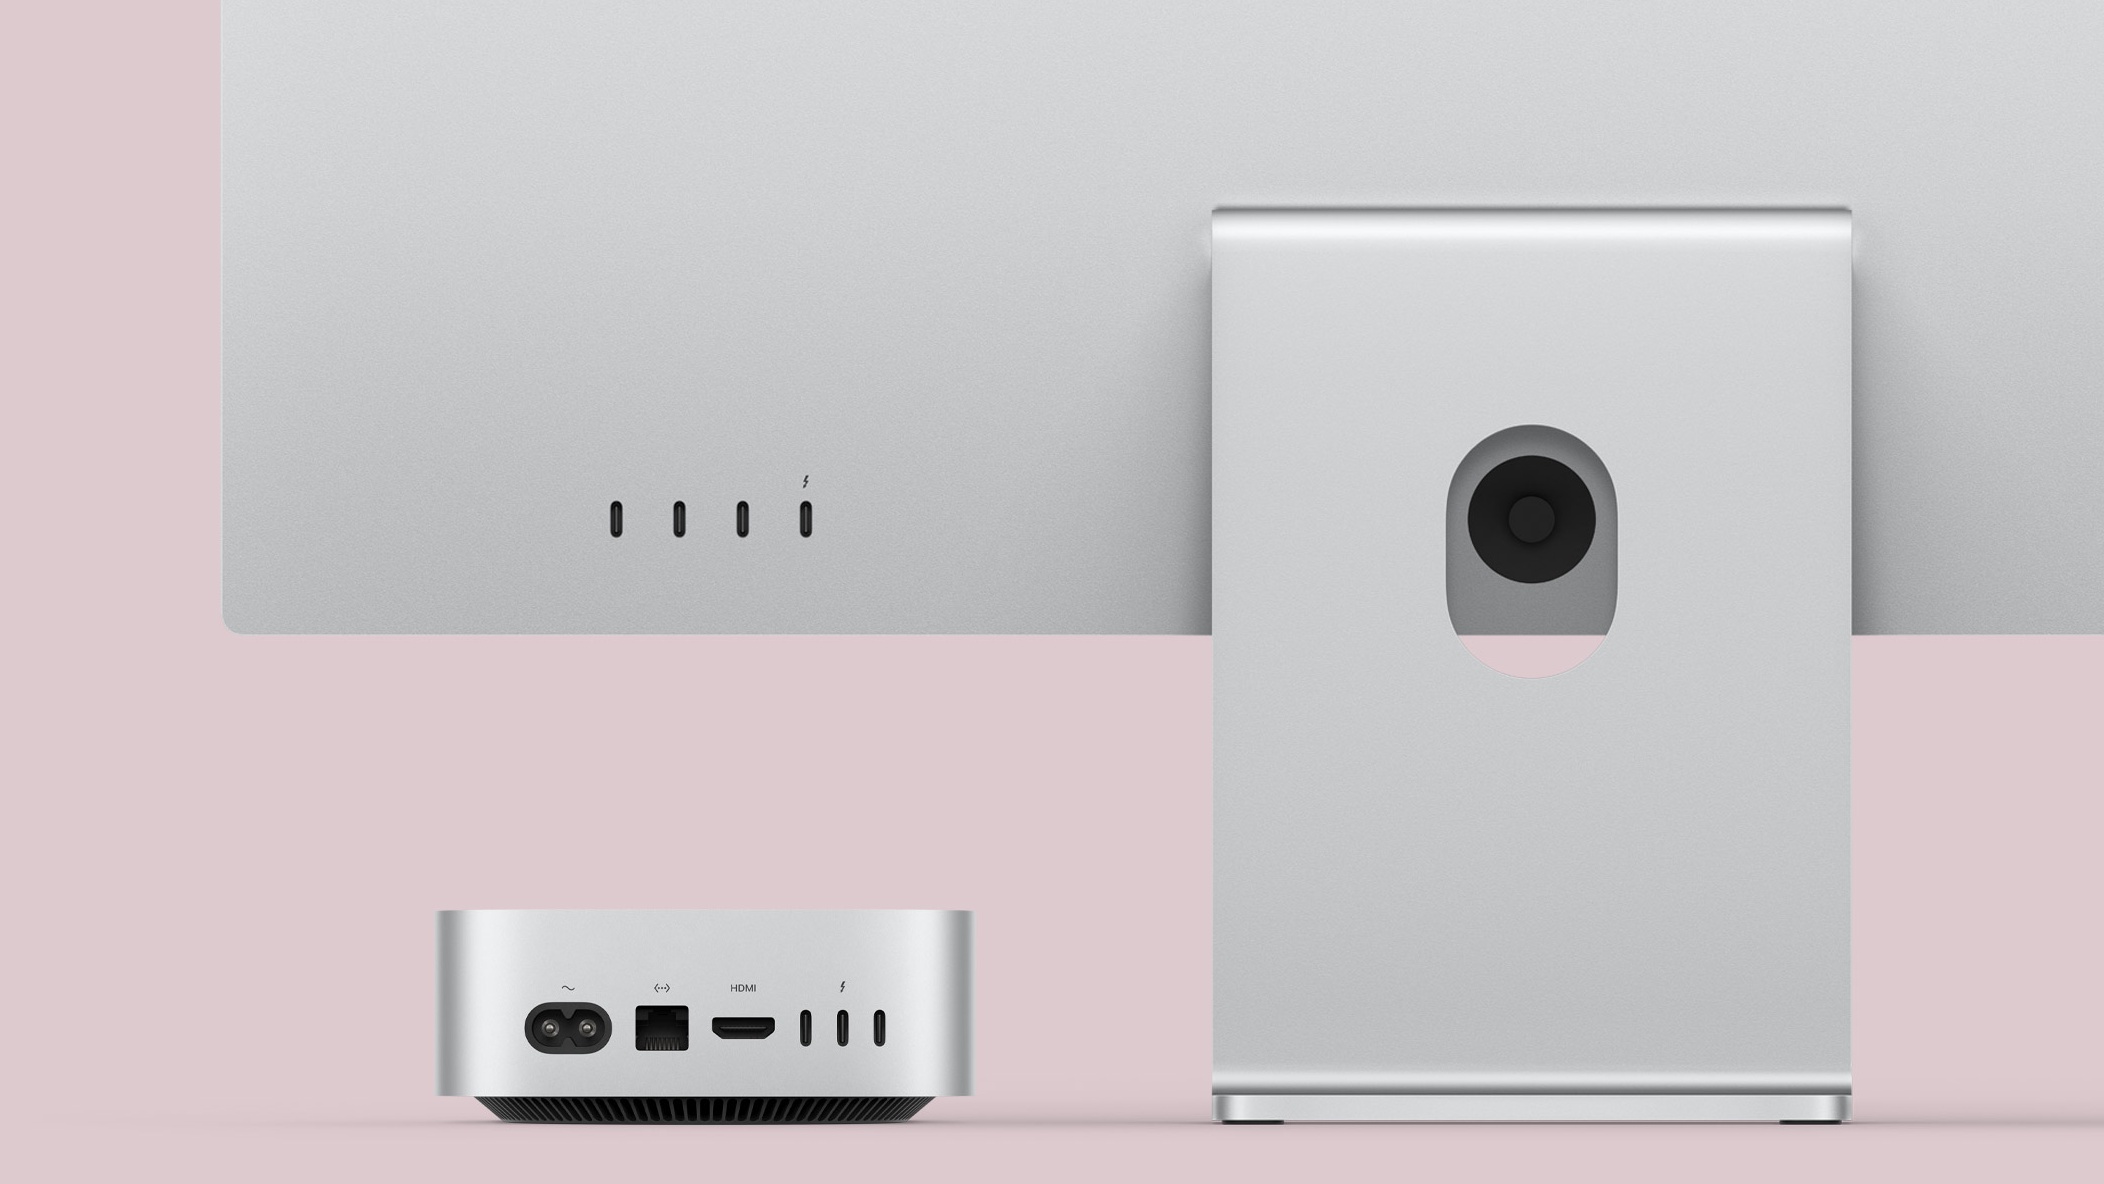
Image showing the back of the M4 Mac mini

(Image credit: Apple)

We’ve also been testing the new M4-powered Macs from Apple – and it's fair to say that we're impressed. And then some…

For instance, our Apple iMac 24-inch review describes the new model as the “best all-in-one computer you can purchase”, a fact helped by its new more affordable price, while our Apple MacBook Pro 14-inch review labeled the laptop “a pro-grade portable that impresses in every area.”

It’s no surprise then that both of those computers were awarded scores of 4.5/5 scores, but we want a step higher for the revamped Mac mini, awarding it one of our rare five-star reviews.

Per our Managing Editor of Core Tech Matt Hanson in our Apple Mac mini review, “Apple has made what was already the best small form factor PC even better thanks to a more compact design, and it packs the new M4 and M4 Pro chips – all while offering incredible value for money as well. I can't recommend this Mac enough.”


from TechRadar - All the latest technology news https://ift.tt/QUTm72H

UK cybersecurity workers earn an average of £87,204 a year, 18% earn £150,000+ But 55% lie awake at night with stress – more than last y...


  • UK cybersecurity workers earn an average of £87,204 a year, 18% earn £150,000+
  • But 55% lie awake at night with stress – more than last year
  • Workers see AI as a threat and a solution

Britain’s cybersecurity workers are earning more than ever after significant wage growth in recent years, even outpacing inflation, a new report has claimed.

Figures from the Chartered Institute of Information Security paint a positive picture for cybersecurity professionals given the tough current financial landscape, however they’re also facing higher stress levels and job pressures than before.

UK cybersecurity professionals are now earning an average of £87,204 a year – more than double the national average of £34,900.

Cybersecurity pays well

Since the Chartered Institute of Information Security’s first report in 2016/17, the industry’s salaries have risen by 29%, which is more than inflation in the same period. Accounting for inflation, salaries have risen a healthy 7% since then.

Top-tier earners also saw greater potential for economic boosts, with nearly one in five (18%) taking home more than £150,000, compared with 7% when the study first started.

However, the financial gain comes at a significant personal cost, with more than half (55%) admitting that job-related stress keeps them awake at night, a climb of five percentage points from last year’s study. Four in five (39%) also shared fears about serious health impacts, like a heart attack.

Around one in five (21%) cybersecurity professionals confirmed that they felt overworked, with the ongoing skills shortage adding to their pressure. In fact, people issues like staffing and skills were raised by 72% of respondents – far more than those who mentioned operational (17%) and technological (11%) concerns.

Besides the lack of people, cybersecurity workers noted a lack of diversity, highlighting that only one in ten are women.

“If the cybersecurity industry wants to attract and keep its talent, it must diversify recruitment practices, hiring based on skills rather than experience or qualifications," noted CIISEC CEO Amanda Finch.

Moreover, the study detailed a mixed response to AI’s role in the industry – 89% see it as benefiting adversaries, while 71% acknowledge its potential for defending networks. However, this is just one of many studies to highlight the lack of policies to manage AI-related risks, with 44% stating that their company needs one.

Finch added: “The security industry needs to build knowledge of the threats posed by AI – particularly GenAI – while it’s still in its relative infancy.”

You might also like


from TechRadar - All the latest technology news https://ift.tt/2Tp9ZCR

Generative AI is evolving. Knowledge-based applications like AI chatbots and copilots are giving way to autonomous agents that can reason ...

Generative AI is evolving. Knowledge-based applications like AI chatbots and copilots are giving way to autonomous agents that can reason and perform complex, multistep workflows. These are powered by what is known as agentic AI. This latest development in AI is poised to transform the way businesses operate by being able to understand context, set goals, and adapt actions based on changing conditions.

With these capabilities, agentic AI could perform a whole range of tasks previously thought impossible for a machine to handle – such as identifying sales targets and making pitches, analyzing and optimizing supply chains, or acting as personal assistants to manage employees’ time.

Amazon's recent partnership with Adept, a specialist in agentic AI, signals a growing recognition of the systems’ potential to automate diverse, high complexity use-cases across business functions. But to fully leverage this technology, organizations must first face several challenges with the underlying data – including latency issues, data silos and inconsistent data.

The three foundations of agentic AI

For its complex functions to operate successfully, agentic AI needs three core components: a plan to work from, large language models (LLMs), and access to robust memory.

A plan allows the agent to execute complex, multi-step tasks. For instance, handling a customer complaint might involve a predefined plan to verify identity, gather details, provide solutions, and confirm resolution.

To follow this plan, an AI agent can use multiple LLMs to break down problems and perform subtasks. In the context of customer services, the agent could call on one LLM to summarize the current conversation with the customer, creating a working memory for the agent to refer to. A second LLM could then plan the next actions, and a third could evaluate the quality of these actions. A fourth LLM could then generate the final response seen by the user, informing them of potential solutions to their problem.

And just like humans, agentic AI systems can’t make informed decisions without using memory. Imagine a healthcare assistant AI with access to a patient's medical history, medical records, and past consultations. Remembering and drawing from this data allows the AI to provide personalized and accurate information, explaining to a patient why a treatment was adjusted or reminding them of test results and doctor's notes.

Both short term and long-term memory is needed for tasks requiring immediate attention, and to build an understanding of context that the AI can rely on for future inferences. But here lies one of the major barriers preventing optimization of agentic AI today: often, businesses’ databases aren’t advanced enough to support these memory systems, limiting the AI's potential to deliver accurate and personalized insights.

The data architecture needed to support AI agents

The predominant approach for meeting memory system requirements is the use of special-purpose, standalone database management systems for various data workflows. However, the practice of using a complex web of these standalone databases can hurt an AI’s performance in a number of ways.

Latency issues arise when each of the different databases used have varying response times, causing delays that can disrupt AI operations. In addition, data silos, where information is isolated in separate databases, prevent the AI from having a unified view and hinder comprehensive analysis, leading to the agent missing connections and providing incomplete results. And on a more fundamental level, inconsistent data—due to variations in quality, formatting, or accuracy—can also cause errors and skew analysis, leading to faulty decision-making. The use of multiple single-purpose database solutions also create data sprawl, complexity and risk, making it difficult to trace the source of AI hallucinations and debug incorrect variables.

Many databases are also not well-suited for the speed and scalability required by AI systems. Their limitations become more pronounced in multi-agent environments, where rapid access to large volumes of data (e.g. through LLMs) is essential. In fact, only 25% of businesses have high-performance databases capable of managing unstructured data at high speed, and just 31% have consolidated their database architecture into a unified model. These databases will struggle to meet GenAI’s demands, let alone support any form of unconstrained AI growth.

As GenAI evolves and agentic AI becomes more prevalent, unified data platforms will become central to any successful AI implementation by organizations. Updated data architectures provide benefits by reducing latency with edge technology, efficiently managing structured and unstructured data, streamlining access, and scaling on demand. This will be a key development in building cohesive, interoperable, and resilient memory infrastructures and allowing businesses to finally capitalize on the automation, precision, and adaptability that agentic AI has to offer.

Embracing the AI revolution

Agentic AI opens the door to a new era where AI agents act as collaborators and innovators, fundamentally changing how humans interact with technology. Once businesses have overcome the challenges associated with disparate data sources and optimized memory systems, they will unlock widespread use of tools that can think and learn like humans, with unprecedented levels of efficiency, insight, and automation.

We've featured the best SQL online courses.

This article was produced as part of TechRadarPro's Expert Insights channel where we feature the best and brightest minds in the technology industry today. The views expressed here are those of the author and are not necessarily those of TechRadarPro or Future plc. If you are interested in contributing find out more here: https://www.techradar.com/news/submit-your-story-to-techradar-pro


from TechRadar - All the latest technology news https://ift.tt/nG9pDjW

A PlayStation patent for a controller with a rewind button has been spotted It could allow players to quickly undo mistakes in-game and t...

  • A PlayStation patent for a controller with a rewind button has been spotted
  • It could allow players to quickly undo mistakes in-game and try again
  • It also seems to have multimedia applications

A patent submitted by Sony for a PlayStation controller with a dedicated rewind button has recently been published.

Available for public viewing at PatentScope - and discovered by Tech4Gamers - the patent shows that the rewind button would be situated where the Share button is on a DualSense Wireless Controller (that's just to the right of the d-pad). The feature would seemingly allow players to rewind their gameplay in order to go back on a mistake or try a section of a level again, for example.

The standout quote from the patent is: "The user is able to enter the rewind mode from the live game play using one or more controller inputs to view recent game play (e.g. rewinding, fast-forwarding, playing, etc.), and returning to live game play afterwards."

The button would not just be for rewinding, then; it seems like it may also allow for fast-forwarding - handy if you're dying to get through those unskippable cutscenes. The patent also described that the button could display "a list of features for the user, such as the rewind mode, a sharing mode for generating a file including a portion of game play that the user would like to share with others, a highlight reel mode that is used to generate a highlight reel of game play, etc."

The concept itself is nothing new; emulators on PC and mobile have had features like save states and fast-forward options since what feels like the dawn of time. Even Nintendo Switch Online's retro libraries offer a simple rewinding system during gameplay. However, this would likely be the first time such a feature has been implemented directly into a piece of hardware from a major console manufacturer.

And of course, it's worth noting that patents aren't sacrosanct. While a neat idea, it would need to be reserved for future iterations of PlayStation hardware - potentially PS6 and its official controller - and even then there's no guarantee. Beyond that, the rewind feature will need to be disabled for online multiplayer games for obvious reasons.

You might also like...


from TechRadar - All the latest technology news https://ift.tt/v3WK82X